> ## Content Index
> Fetch the complete content index at: https://blog.quimerax.com/llms.txt
> Use this file to discover other available public pages before exploring further.
# BTMOB Exposed: Inside a Fraud-as-a-Service Platform with 1400+ live servers
- URL: https://blog.quimerax.com/btmob-exposed-inside-a-fraud-as-a-service-platform-with-1400-live-servers/
- Published: 2026-08-17T21:01:50.000Z
- Updated: 2026-08-17T21:27:59.000Z
- Author: QuimeraX Team
## The Trail
In February 2023, cryptocurrency payment processor **Freewallet** froze roughly $75,000 in accumulated earnings from a customer in Syria. The company demanded KYC verification. That moment of financial friction cracked the operational security that a threat actor known as **EVLF** had maintained for approximately eight years, and gave cybersecurity firm **[CYFIRMA](https://www.cyfirma.com/research/unmasking-evlf-dev-the-creator-of-cypherrat-and-craxsrat/?ref=blog.quimerax.com)** the thread they needed to unravel one of the most prolific Android RAT operations on the market.
**EVLF** (also known as **EvilWolf**, or **"EVLF DEV"**) had been building and selling Android remote access trojans from Syria since roughly 2015\. His first publicly tracked products were **CypherRAT** and **CraxsRAT**, distributed through a surface-web shop and a Telegram channel (**`@craxso`**) that accumulated over 10,000 subscribers. Over three years, an estimated 100 or more threat actors purchased lifetime licenses. The ecosystem eventually fractured when buyers began releasing cracked versions for free, a pattern that would repeat, almost identically, with BTMOB.
The lineage from CraxsRAT to BTMOB runs through an intermediate family called **SpySolr**. Multiple independent analyses (Cyble, ESET, ANY.RUN, Mallory.ai) confirm that BTMOB is an evolution of SpySolr, itself derived from the CraxsRAT codebase. The architectural "DNA" is unmistakable: the same Accessibility Service abuse patterns, similar WebSocket-based C2 communication, overlapping command structures. But BTMOB represented a leap in ambition: from a general-purpose RAT to a purpose-built banking fraud platform with a professional operator experience.
When **[Cyble Research](https://cyble.com/blog/btmob-rat-newly-discovered-android-malware?ref=blog.quimerax.com)** and **Intelligence Labs (CRIL)** published the first public analysis on February 12, 2025 (based on a sample discovered January 31), the malware was at version **BT-v2.5.** It was distributed as **`lnat-tv-pro.apk`** through a phishing site impersonating iNat TV, a Turkish streaming platform.
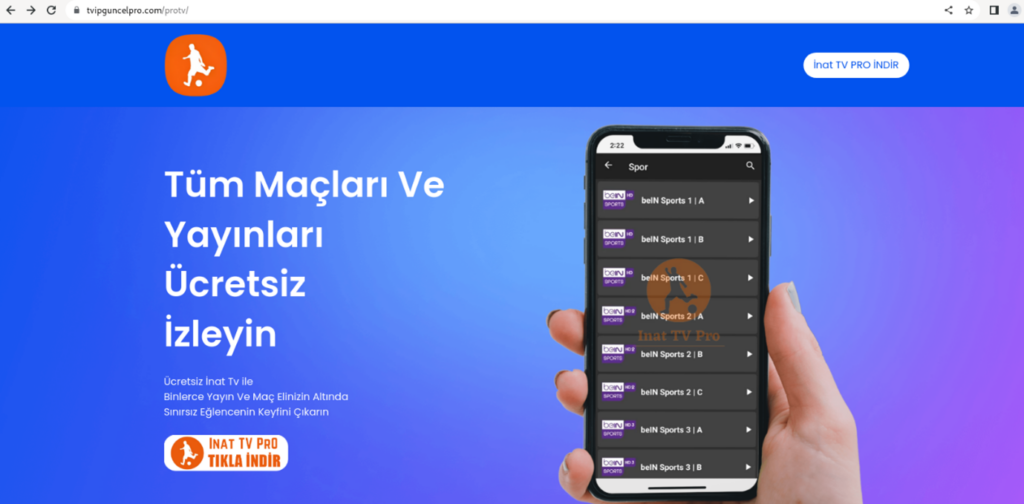
*Figure 1: BTMOB distributed via a fake iNat TV site. Source: Cyble.*
The C2 server resolved to **`hxxp://server[.]yaarsa[.]com/con`**. That domain, **yaarsa**, persists as the name of the backend directory in every leaked source package we analyzed. The entire C2 backend still lives under **`/yaarsa/private/`**, the database is still called **`clients`**, and every PHP handler still follows the **`yarsap_NNNNN.php`** naming convention established when **`yaarsa[.]com`** was the canonical server.
**The infrastructure moved on. The code remembers.**
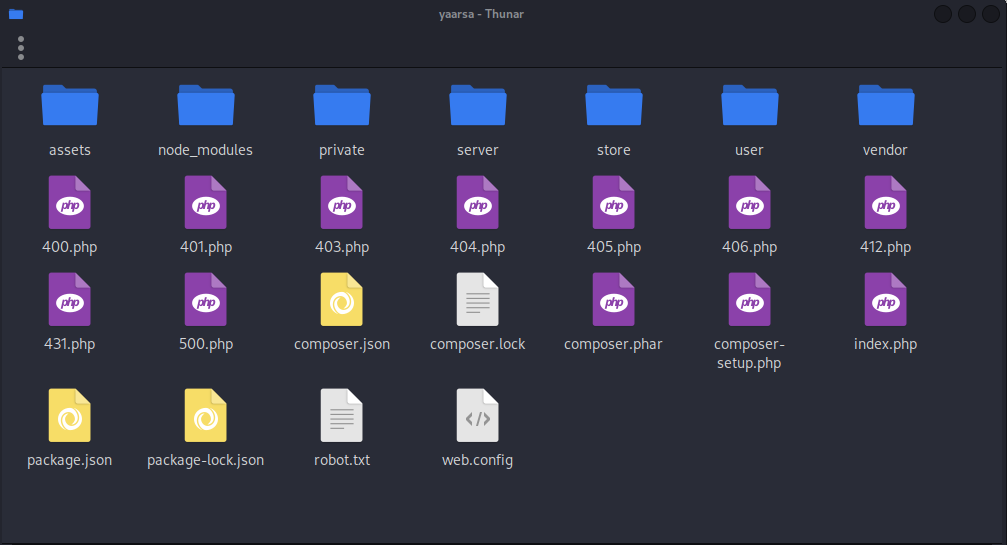
*Figure 2: The *yaarsa* directory from the leaked source, the backend structure that persists across every analyzed package.*
Since then, BTMOB has continued to evolve. We obtained the source code packages for versions **4.5.7** and **4.6**, which together comprise the full operator kit: the **VB.NET operator panel** (80 `.vb` files), the **server-side APK builder pipeline** (SolrStarter/SolrWorker .NET executables), the **complete Android source tree** (101 Java files: genuine development source, not a decompile), **the dropper**, and the **entire C2 backend.**
What the source code reveals goes beyond feature additions. It reveals a structural transformation from a centralized operation into a self-service criminal franchise, complete with a reseller API, whitelabel branding, automated APK generation, and capabilities that extend far beyond banking fraud into DDoS, cryptomining, and network exploitation.
This report traces BTMOB from its roots in a Syrian developer's earlier malware projects to its current form as a full-featured Android attack platform, and documents what the leaked source code reveals.
## The Developer Speaks
EVLF operates the official Telegram account **`@CRAXSO`** and maintains a surface-web storefront at **`btmobrat[.]net`.** This storefront funnels visitors straight to Telegram: a "Join us on Telegram" button links to the operation's community of three group chats.
*Figure 3: The BTMOB Telegram community: three group chats linked directly from the *btmobrat\[.\]net* storefront*
The FAQ message in one of the Telegram groups states that the developer of BTMOB is "EVLF (EvilWolf), owner and administrator of the official Telegram channel @CRAXSO" and that he is "exclusively present in this channel."
The FAQ also addresses a drama that speaks directly to the platform's fragmentation: an impersonator using the handle **`@btmobadmin`** reportedly bought the source code and began releasing customized versions while claiming to be the original developer. According to the FAQ, this has been ongoing for over two years. This is not an isolated incident; it's the inevitable consequence of selling source code access for a tool with an established reputation.
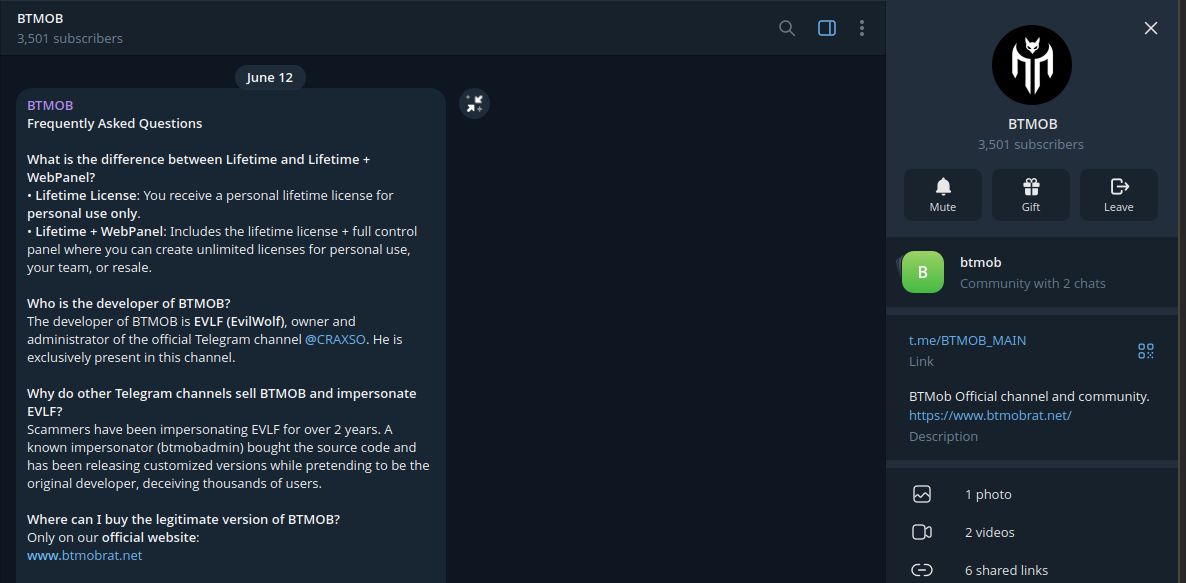
*Figure 4: BTMOB's official Telegram FAQ addressing impersonation. Evidence of the platform's fragmentation, straight from the operator.*
*Figure 5: EVLF *(@CRAXSO)* Telegram account on August 12, 2026.*
## The Real Price of Source Code
BTMOB's pricing history reads like a startup's pivot narrative, except the product is a banking trojan.
| Date | Product | Price |
| ------------------ | --------------------------- | ---------------- |
| Jan 2025 | Monthly subscription | $700/mo |
| Jan 2025 | Lifetime license | $3,000 |
| Jan 2025 | Private infra + support | $5,000 + $300/mo |
| May 2025 | Full source code | $20,000 |
| Dec 2025 | Source code (reduced) | $10,000 |
| Apr 2026 (V4.5) | Lifetime account | $1,200 |
| Apr 2026 (V4.5) | Private server (multi-acct) | $3,000 |
| Apr 2026 (V4.5) | Server source code | $7,000 |
| Aug 2026 (current) | Lifetime | $700 |
| Aug 2026 (current) | Source code | $2,000 |
| Secondary market | Lifetime access | $500 |
| Secondary market | Source code | $1,500 |
| Secondary market | Lifetime + custom branding | $800 |
The price trajectory tells a story of market pressure. As cracked and leaked versions proliferated, official prices plummeted. Multiple leak events accelerated the fragmentation: source packages began circulating on underground forums and Telegram channels in mid-2025, and in January 2026 BTMOB v3.6.3 source code appeared on a dark web forum. Around the same time, the v4.x packages we analyzed (containing the full backend and the complete operator kit) became available through secondary distribution channels.
## From Product to Franchise
The source code reveals the exact moment the business model changed.
In **`btlogin.php`**, the **HWID (Hardware ID)** enforcement that once locked each operator account to a single machine is commented out. Not deleted. Commented out. The V3.2 changelog from April 13, 2025 makes it explicit: "Disabled BTMOB device hardware lock, you can now change your PC anytime."
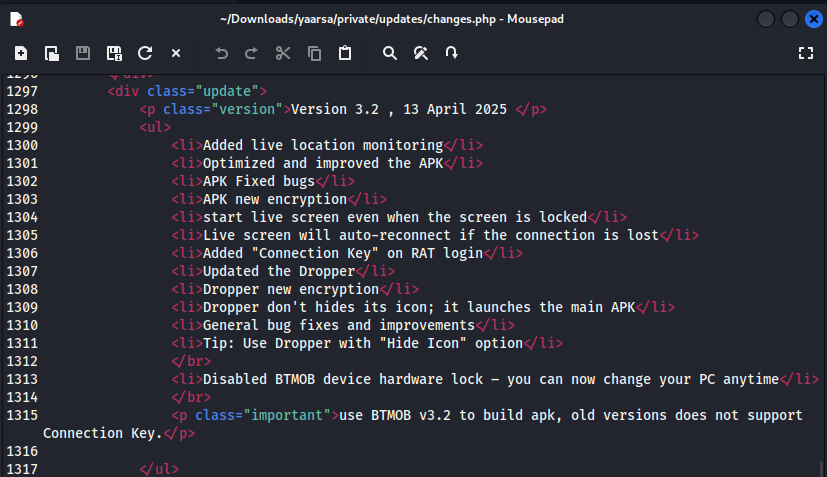
*Figure 6: Operator changelog extracted from *yaarsa/private/updates/changes.php.**
This wasn't a bug. It was a business decision. By removing HWID binding, EVLF transformed BTMOB from a locked-down, centralized service into a portable product that buyers could run on any machine, and critically, resell.
The backend confirms the new model. A resellers table with sellerkey authentication allows third parties to create operator accounts, issue activation codes, and collect USDT cryptocurrency payments.
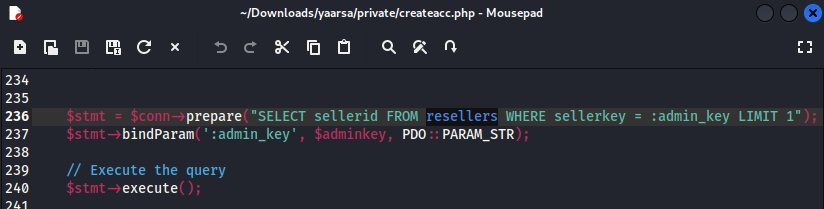
*Figure 7: Reseller authentication in *yaarsa/private/createacc.php*: the SQL query that validates third-party seller keys against the *resellers* table.*
Today, BTMOB no longer signifies a unified operation. It's a brand name attached to a freely available codebase, operated by an unknown number of independent actors with varying levels of competence and intent.
## BTMOB Lands in Brazil
Brazil has always been fertile ground for Android banking malware. With Pix (the country's instant payment system) processing over 40 billion transactions in 2025, high smartphone banking adoption, and a vibrant and fragmented cybercrime underground, the market was waiting for a tool like BTMOB.
The platform's arrival in Brazil followed the same franchise pattern visible elsewhere: local operators acquired the tool, customized it for Brazilian targets (bank overlays, Portuguese-language lures, Pix-specific flows), and distributed it to downstream buyers. [ThreatFabric](https://www.threatfabric.com/blogs/phantomcard-new-nfc-driven-android-malware-emerging-in-brazil?ref=blog.quimerax.com) documented one such operator: a threat actor known as go1ano (also tracked as "go1ano Developer"), who claimed to be a "trusted partner" of both BTMOB and the GhostSpy spyware family. [OSINT Industries'](https://www.osint.industries/project/the-go1ano-case-osint-in-brazils-malware-ground-zero?ref=blog.quimerax.com) investigation into go1ano mapped a dual-identity pattern connecting legitimate professional activity to cybercrime operations, with domain registrations dating back to 2015 and appearances in eight data breaches between 2015 and 2025.
Go1ano is not an isolated case. Advisory pages associated with the BTMOB brand list hundreds of blacklisted accounts accused of falsely reselling the platform, a number that speaks less to effective policing and more to the scale of unauthorized distribution.
The builder ships with 14 pre-made lure templates impersonating popular apps (Netflix, WhatsApp variants, AdBlocker, Snaptube, Picsart), and the first documented sample targeted Turkish users with a fake iNat TV streaming app. But the Brazilian phishing runs deeper than templates. Observed campaigns distribute BTMOB through polished fake Google Play Store pages targeting every category: package tracking apps impersonating logistics companies like Rodonaves, banking "security modules," streaming services, utility apps. Each clone comes complete with fabricated ratings, thousands of fake reviews in Portuguese, and spoofed data safety sections.
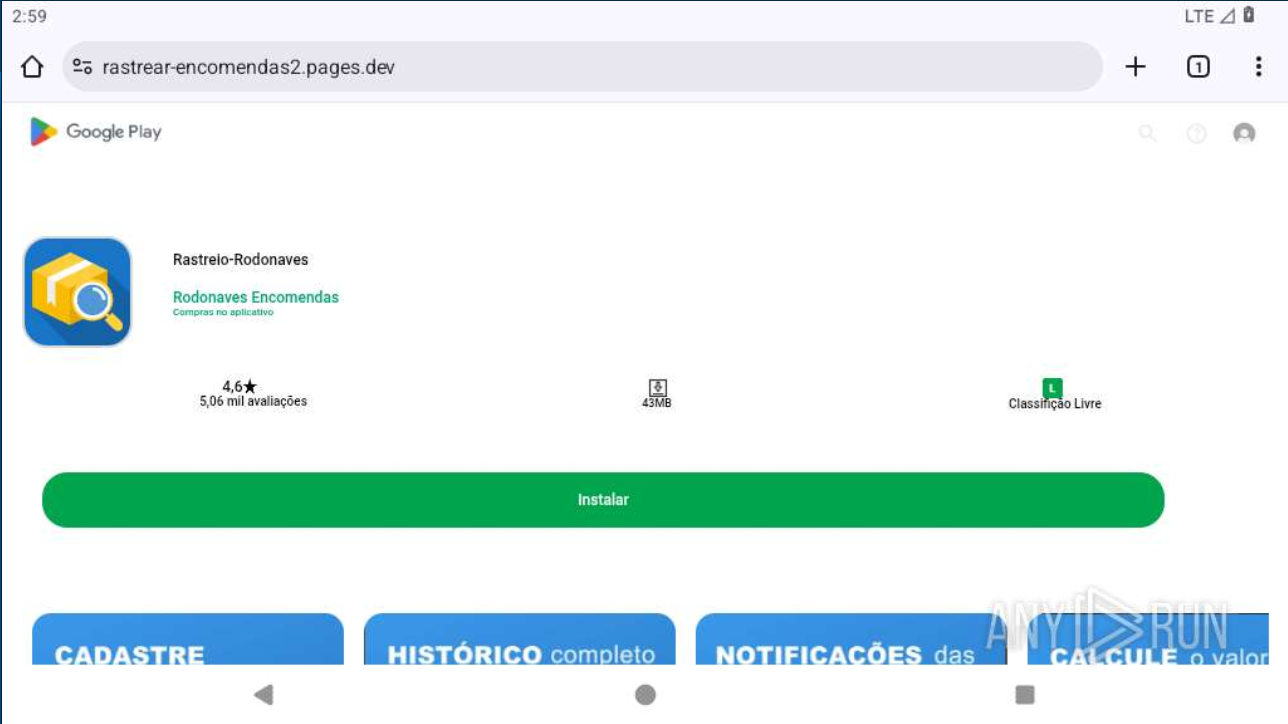
*Figure 8: Fake Google Play page at *rastrear-encomendas2\[.\]pages\[.\]dev*, distributing BTMOB as a Rodonaves package tracking app. Note the fabricated 4.6-star rating and 5,060 reviews in Portuguese. Source: ANY.RUN.*
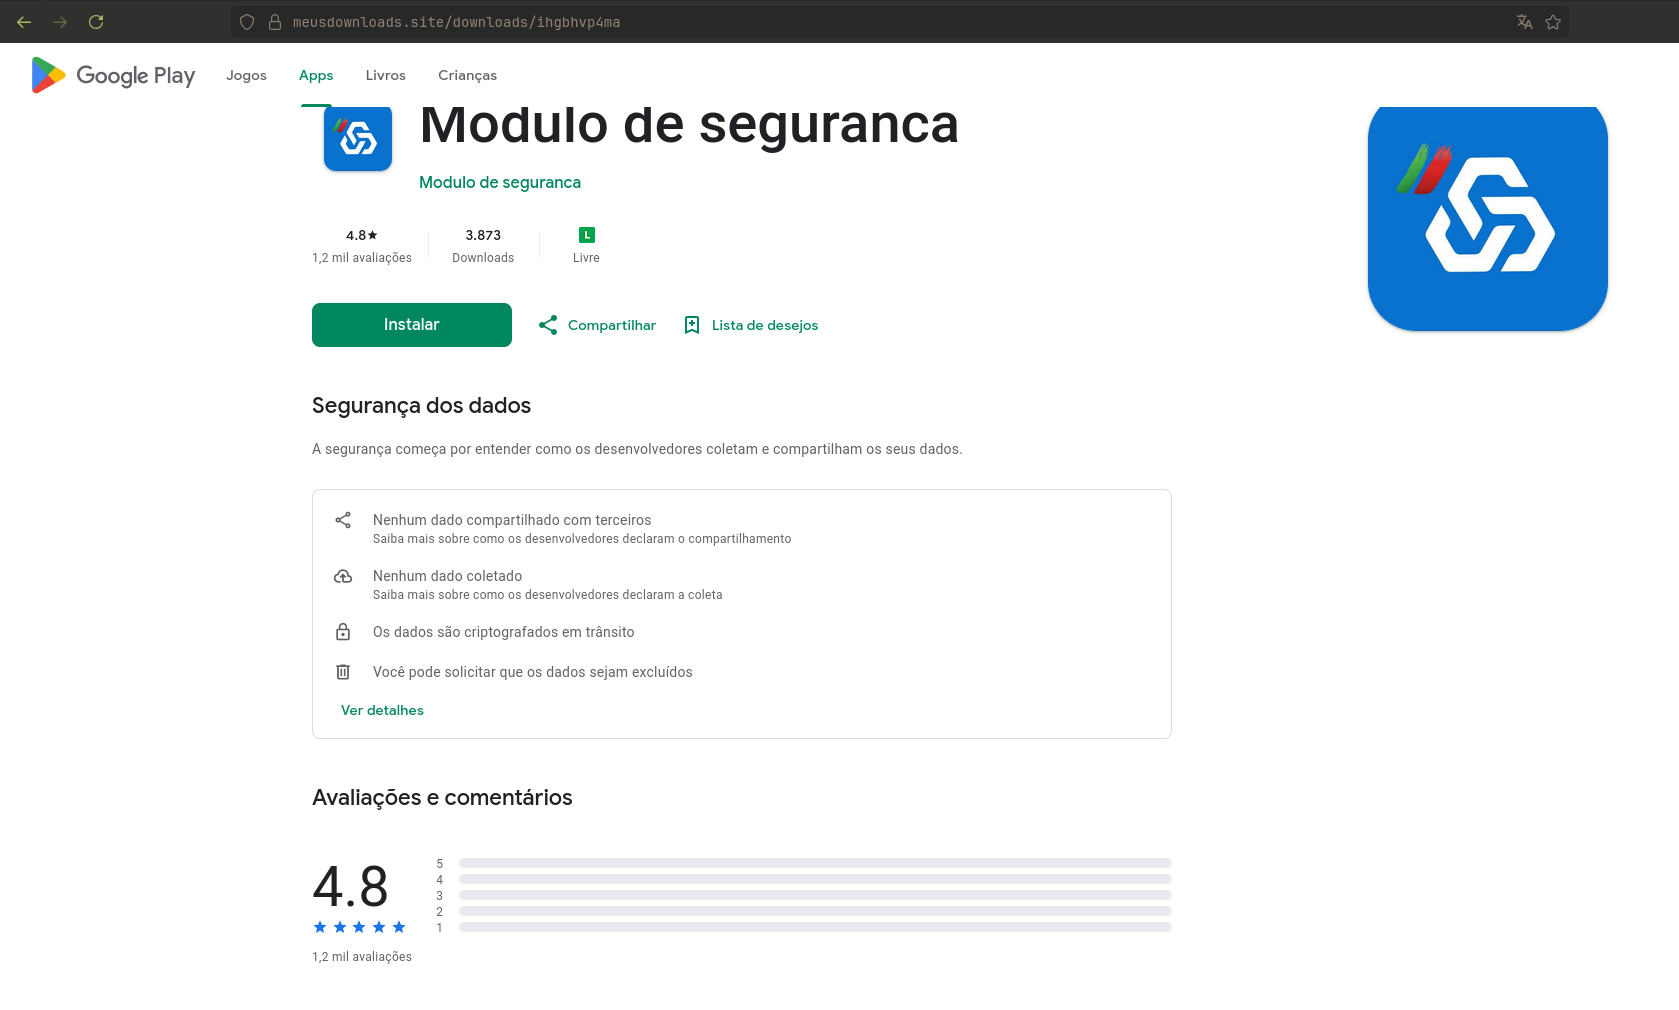
*Figure 9: Active BTMOB distribution page at *meusdownloads\[.\]site*, impersonating the Google Play Store to deliver a fake banking "security module." Note the fabricated 4.8-star rating, 1,200 reviews, and a fake data safety section claiming no data is collected.*
The V3.3 changelog (April 2025) added Spanish and Portuguese accessibility pages, and the dropper includes localization for seven languages: EN, AR, ZH, TR, PT, RU, ES. The Arabic-first localization and right-to-left UI support in the earliest versions are consistent with EVLF's Syrian origin; Portuguese was a later addition driven by market demand.
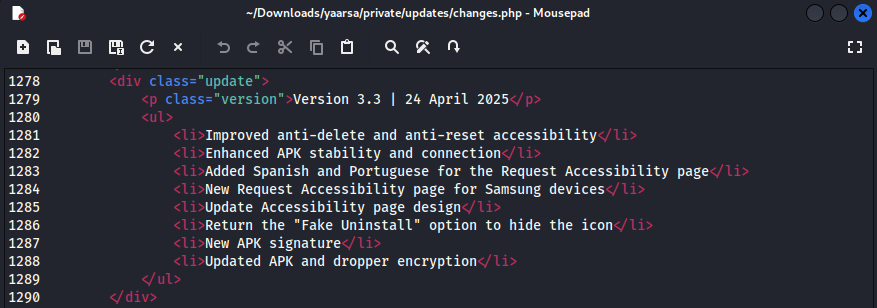
*Figure 10: V3.3 changelog entry in *yaarsa/private/updates/changes.php*: Spanish and Portuguese accessibility pages added on April 24, 2025, marking BTMOB's expansion into Latin American markets.*
## Under the Hood
BTMOB is not a single piece of malware. It's a platform with five interlocking components, all running on a single Windows host under XAMPP.
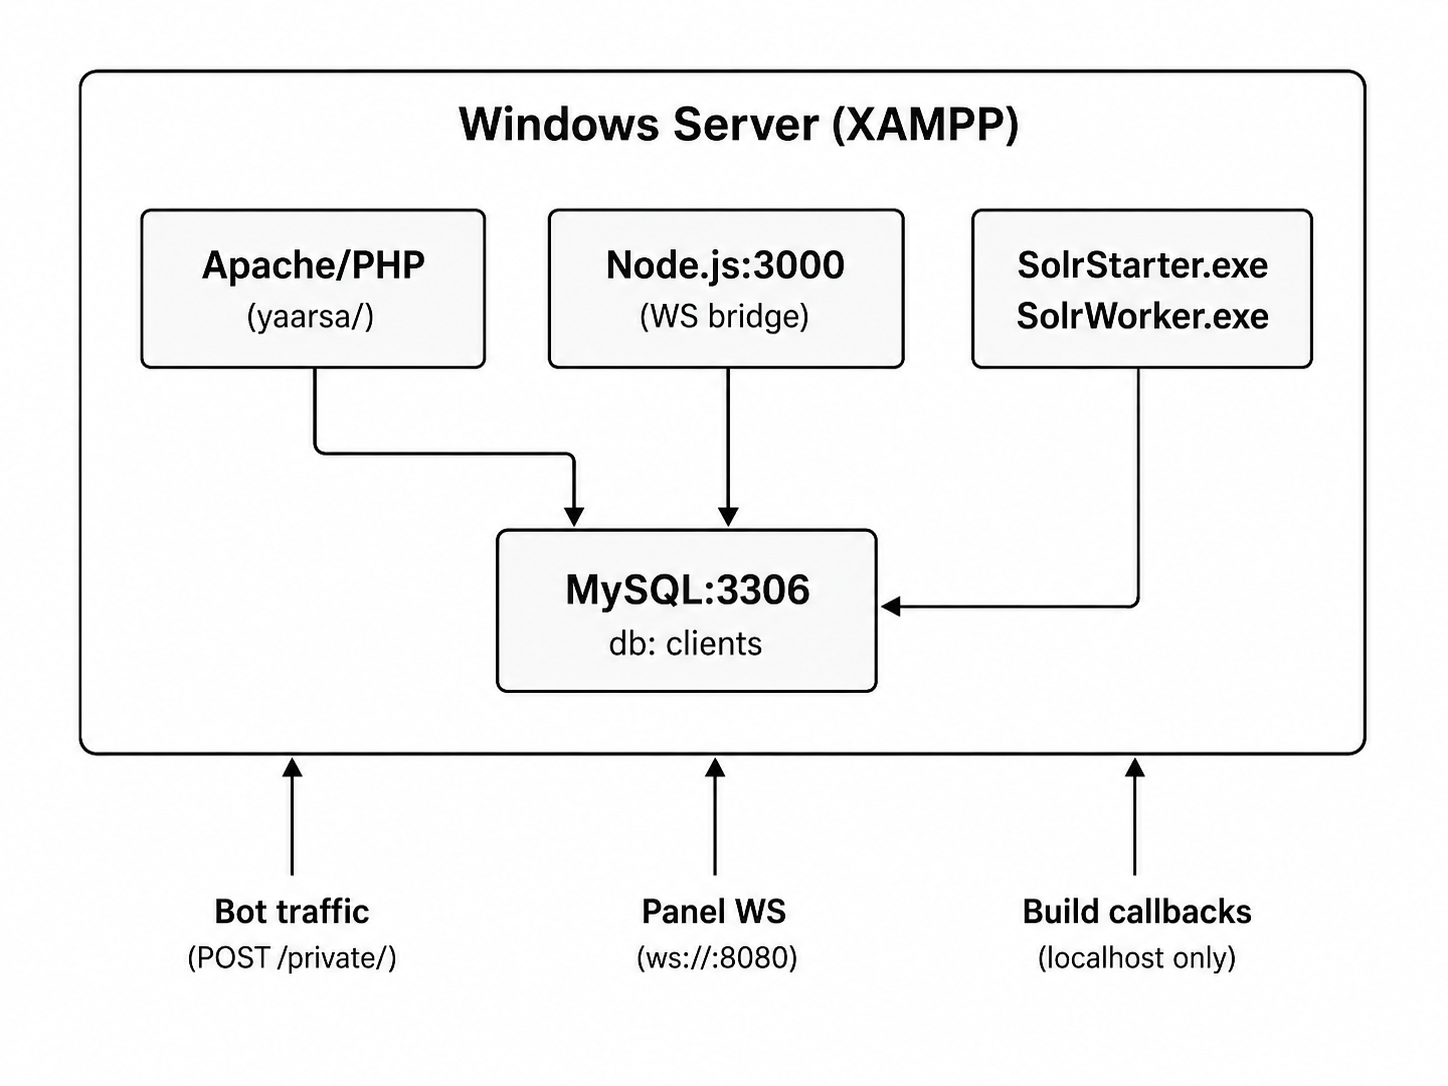
*Figure 11: BTMOB platform architecture: five components on a single Windows/XAMPP host. Bot traffic, operator panel, and APK builder all converge on one MySQL database.*
The **APK payload** (101 Java files, genuine Android Studio source, not a decompile) is the RAT installed on victim phones. The **dropper** is a weaponized fork of Shelter, an open-source app that abuses Android's Work Profile for isolation. The **VB.NET panel** (BTMob.exe) is the operator's desktop console. The **C2 backend** (PHP, MySQL, Node.js) handles 45 endpoints under **`/yaarsa/private/`.** And the **APK builder** (SolrStarter.exe/SolrWorker.exe) is a template-based pipeline: operators fill in a form (app name, icon, C2 address, permissions) and the server produces a ready-to-distribute APK. No development knowledge required.
The design is monolithic by today's standards, but operationally simple: one server, one install, everything works. The target customer is a fraud operator, not a DevOps engineer.
## Hunting
The leaked source code gives defenders something interesting: exact knowledge of what a C2 server looks like from the outside, before ever touching a live host. Hit the server's root URL and you see what looks like a misconfigured Apache installation: a fake 403 Forbidden page with a JavaScript redirect to **`google[.]com`** after five seconds. The actual operational endpoints are buried under **`/yaarsa/private/`**.
### The Fake 403
In **`yaarsa/server/websocket-server.js`**, the `blocksmg` constant defines 18 lines of HTML: a page titled **`403 Forbidden`** with the message **"Redirecting in 5 seconds..."** and a JavaScript redirect to **`google[.]com`** after 5 seconds. The same page is served at the Node.js root route on port 3000\. Near-identical copies appear in **`yaarsa/index.php`** and **`yaarsa/user/login.php`**, with one difference: their JavaScript timer fires in 1 millisecond instead of 5 seconds, despite displaying the same "5 seconds" text.
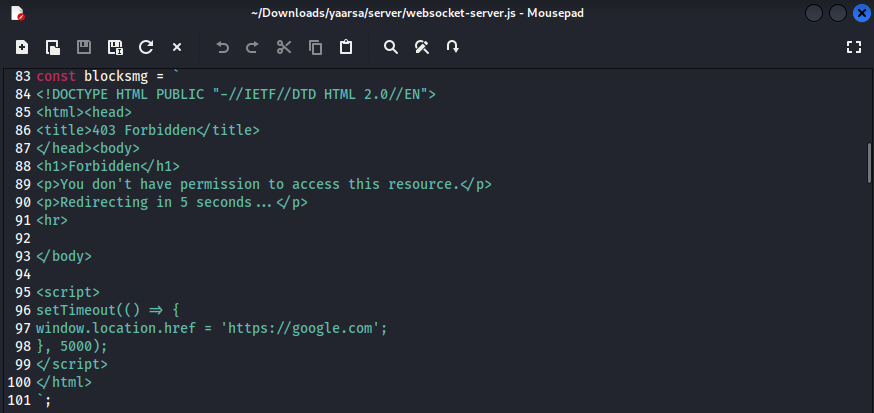
*Figure 12: The *blocksmg* constant in *websocket-server.js*, the fake 403 page served on port 3000.*
### From Source Code to Live Infrastructure
Internet scanning platforms like Shodan, FOFA, Censys, ZoomEye, and Hunter index HTTP responses from every reachable host. Each platform computes its own response fingerprints (Shodan uses **`html_hash`**, FOFA uses **`body_hash`**, Censys indexes full response bodies), and all of them capture the same raw HTML. The same fake 403 page that exists in the source code is searchable across every major scanning platform.
We used Shodan's **`html_hash`** to demonstrate the approach, but the underlying pattern (the fake 403 HTML, the port combination, the IIS default page) is platform-agnostic.
**Port 80** on most BTMOB C2 servers shows the default Windows Server IIS welcome page. This happens because the install guide instructs operators to deploy on Windows Server using XAMPP, but never tells them to disable the IIS service that runs by default. The result is two web servers on the same host: IIS answering port 80 with its stock welcome page, and Apache handling the actual C2 application on other ports.
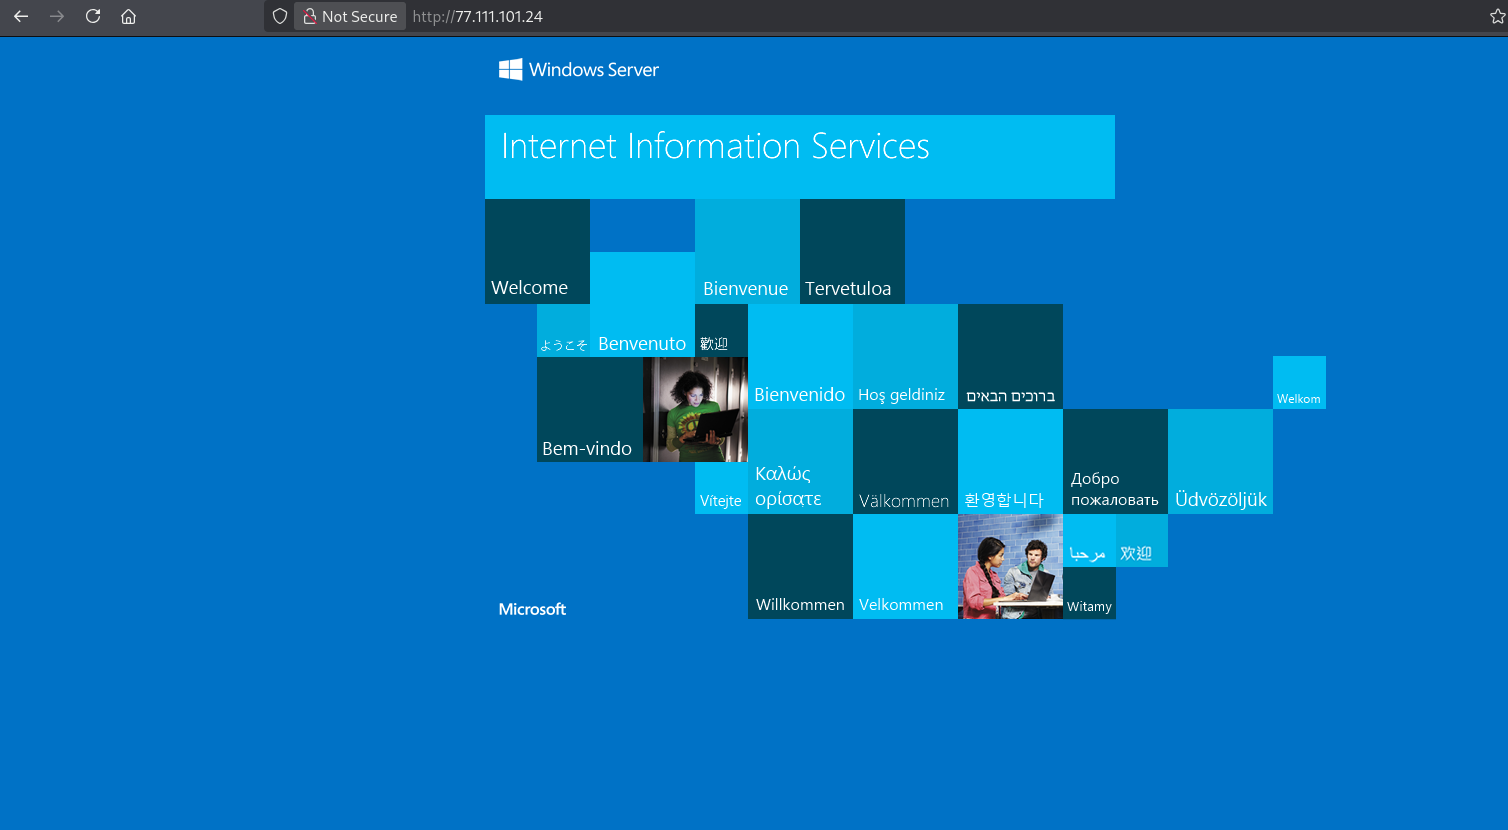
*Figure 13: Port *80* on *77\[.\]111\[.\]101\[.\]24.* Default Windows Server IIS welcome page.*
**Port 3000 is the exposed flank.** The **Node.js/Express** server serves the fake 403 page at its root route, mimicking a default Apache error and a redirect to **`google[.]com`** after 5 seconds.
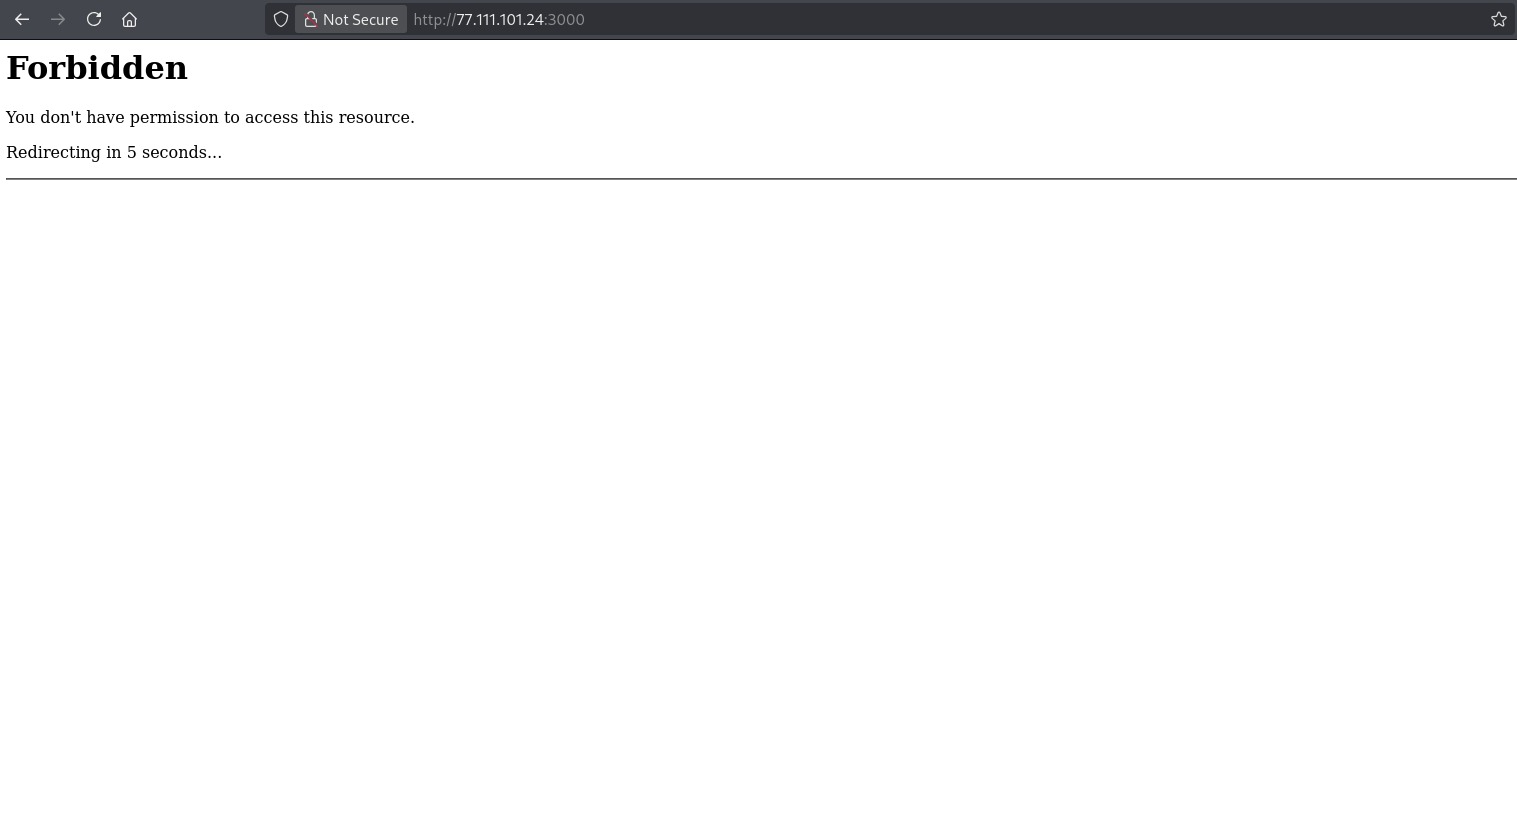
*Figure 14: Port *3000* on *77\[.\]111\[.\]101\[.\]24.* The fake 403 Forbidden page defined in *websocket-server.js*. The HTML mimics a default Apache error, then redirects to *google\[.\]com* after 5 seconds.*
The fake 403 page on port 3000 produces the **`html_hash`** value **`-983012381`.** Searching Shodan:
**`http.html_hash:-983012381 port:3000`**
This returned **1,402 hosts**. The vast majority of them serve the exact HTML defined in the source code: an **HTML 2.0 DOCTYPE** mimicking an Apache error, **`403 Forbidden`**, **"Redirecting in 5 seconds..."**, and a JavaScript redirect to **`google[.]com`.**
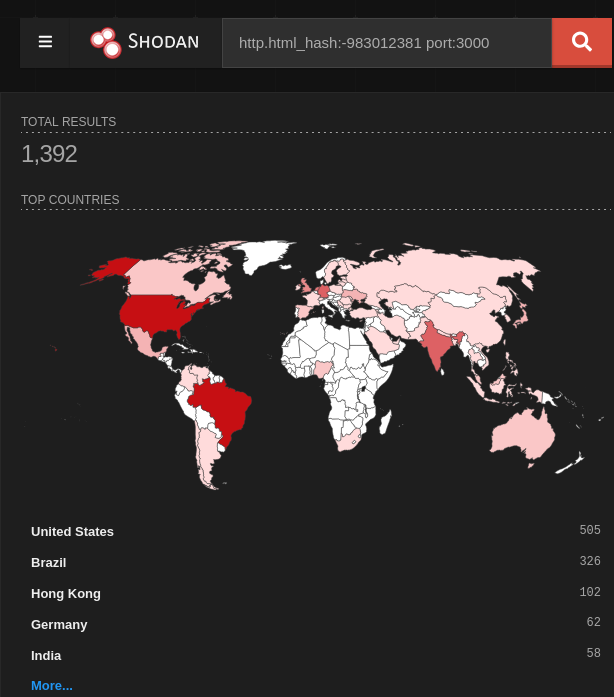
*Figure 15: Shodan results for *http.html\_hash:-983012381 port:3000*. *1,402 hosts*, with Brazil as the second most affected country.*
### Confirming the Match
Among the 1,402 results, we manually verified several hosts and confirmed they are running the full BTMOB stack. The confirmed C2 servers share a consistent port signature. Visiting each port on a confirmed host **`77[.]111[.]101[.]24`** reveals the full stack:
| Port | Service | Behavior |
| ---- | --------------- | -------------------------------------------- |
| 80 | IIS | Default Windows Server welcome page |
| 3000 | Node.js/Express | Fake 403 page (root route) |
| 3306 | MySQL | Database backend |
| 8080 | WebSocket | Returns 426 Upgrade Required on regular HTTP |
| 3389 | RDP | Remote desktop access (operator management) |
The database and remote access layers are equally visible. MySQL on port 3306 responds to external connections, and the WebSocket server on port 8080 reveals itself with a 426 Upgrade Required when accessed over plain HTTP:
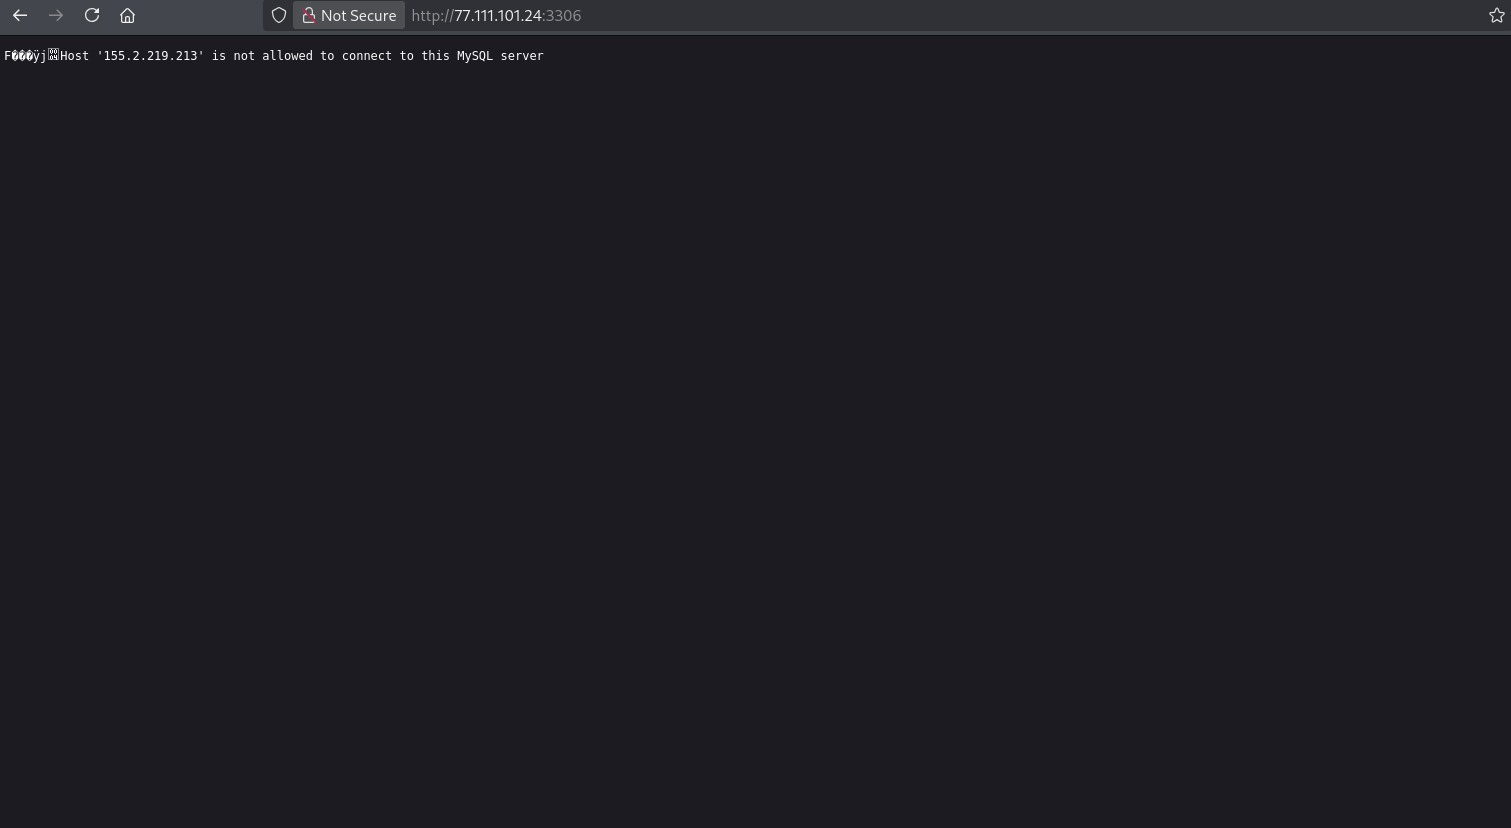
*Figure 16: Port *3306* on *77\[.\]111\[.\]101\[.\]24.* MySQL responds to external connections with a host-based denial, confirming the service is exposed without network-level filtering.*
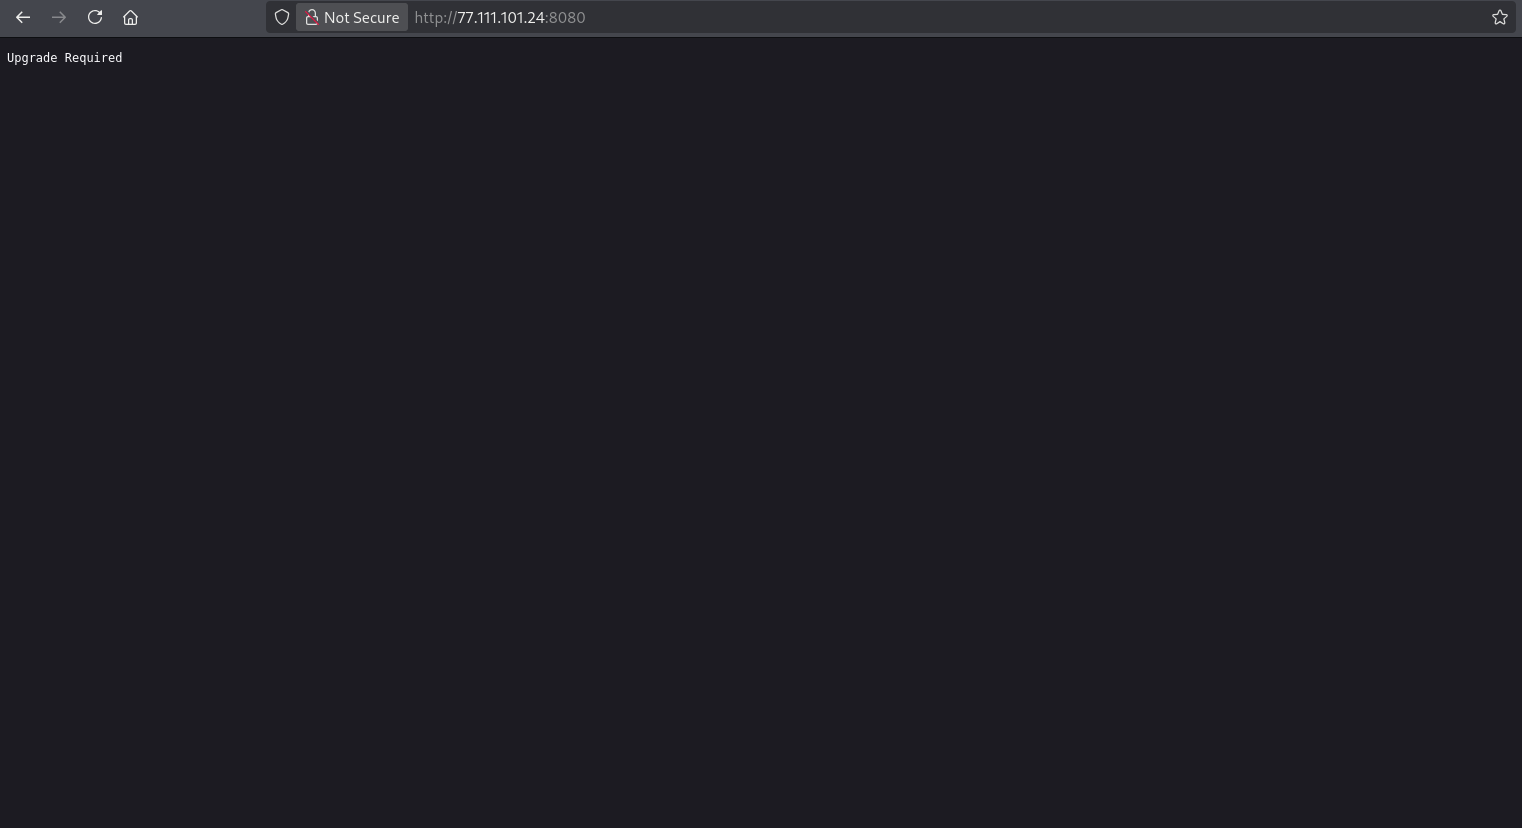
*Figure 17: Port *8080* on *77\[.\]111\[.\]101\[.\]24.* The WebSocket server responds with 426 Upgrade Required when accessed over plain HTTP, confirming the WebSocket endpoint used by both the VB.NET operator panel and infected devices.*
### The Bypass Factory
While scanning Shodan results for BTMOB C2 servers, we noticed several hosts with an unexpected page title: **"painel de controle elite."** These weren't C2 panels. They were something else entirely. A dedicated dork confirmed the pattern:
```
html:"painel de controle elite"
```
This returned **19 hosts**, mostly in Brazil, all running a shared platform called **"Painel de Controle Elite"**. The service runs typically on port 5000, and offers a straightforward workflow: an operator uploads a malicious APK, the service processes it to **evade Google Play Protect**, and returns a modified APK ready for distribution.
The operational security matches the sophistication you'd expect from a drag-and-drop bypass service: the default credentials are **`admin:admin123`**, and most operators never change them. The same login works across multiple live instances, a detail that says less about the platform's security and more about who is running it.
Each operator rebrands the same platform with their own name. At the time of writing, the following instances were live:
| Operator name | Notes |
| -------------------- | ------------------------------ |
| BT Bypass Rat | Direct BTMOB reference |
| ZNT BYPASS + DROPPER | |
| FUD BYPASS | FUD = "Fully Undetectable" |
| APKGOD0 | |
| Bypass do Bender | |
| Siberian KL | KL = keylogger |
| JB KL | |
| OMASSA 171 | 171 = Brazilian slang for scam |
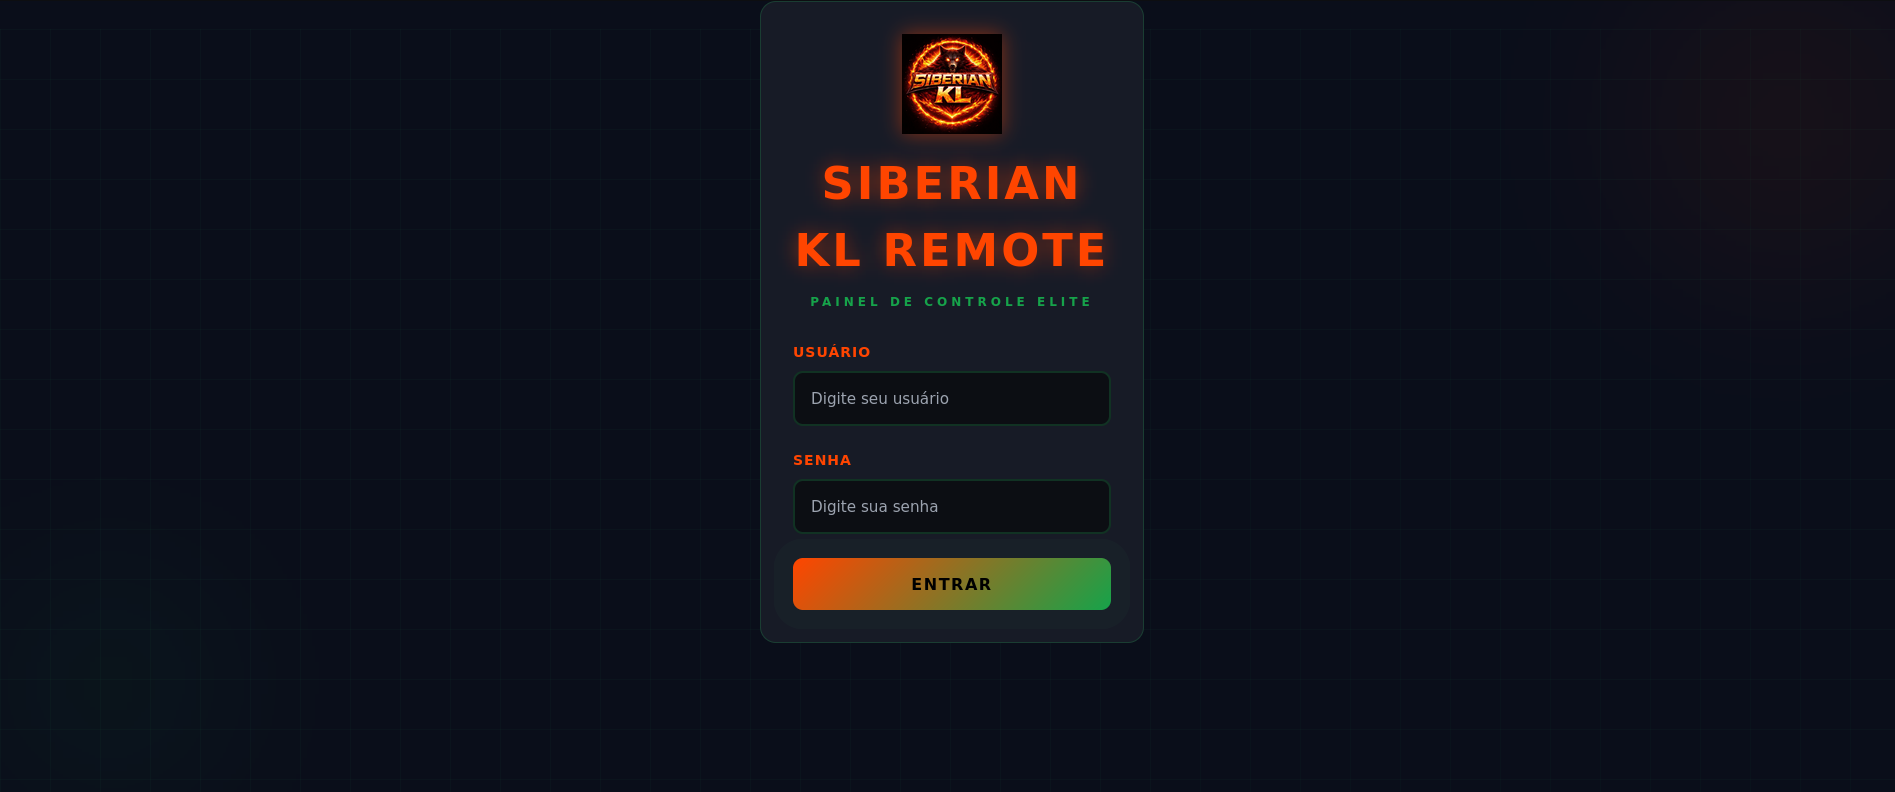
*Figure 18: Login page of a *Painel de Controle Elite* instance branded as *"Siberian KL."**
The panel exposes the full pipeline:
- **APK upload and processing:** operators drag and drop an APK, the service modifies it and returns a bypassed version.
- **Reseller management:** operators can onboard sub-users, track their build history, and revoke access.
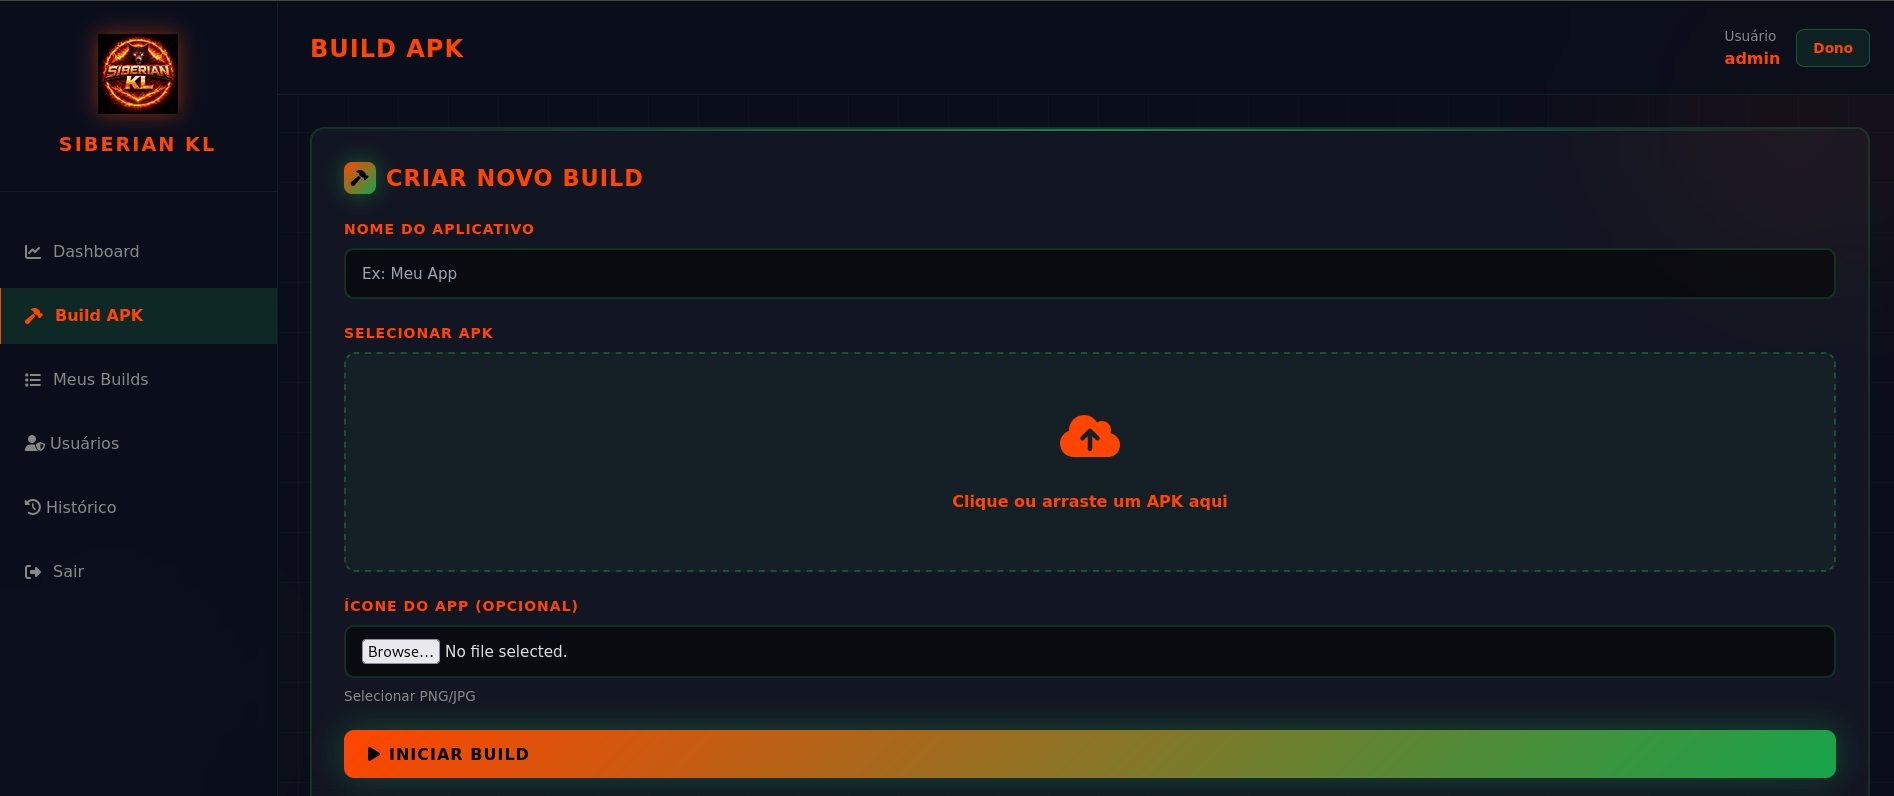
*Figure 19: The *Build APK* page inside the *Siberian KL* panel. Operators upload a malicious APK, the service processes it to evade Play Protect, and returns a bypassed version ready for distribution.*
This is not a RAT command-and-control server. It is the supply chain layer that sits between a RAT builder like BTMOB and the victim's phone: build the APK, upload it here, receive a Play Protect-clean version, push it in many places. The "BT Bypass Rat" instance confirms this platform is being used in the BTMOB ecosystem.
These are only the instances indexed under one shared panel name. The bypass-as-a-service model is generic: any operator can deploy their own instance with a different title, making the visible 19 hosts a lower bound.
### RADAR: Build, Inject, Sign, Distribute
A separate platform we identified during our research operates under the name **RADAR**: a self-described "sistema de processamento Android" (Android processing system) hosted at **`playstoreapps[.]pro`.**
RADAR automates the entire APK weaponization pipeline. An operator uploads a clean APK, and the system handles the rest through seven stages: extract, decode with apktool, prepare the helper, inject the payload, recompile, sign with a keystore, and deliver the final package. The build log streams in real time. No technical knowledge required, the platform says so itself.
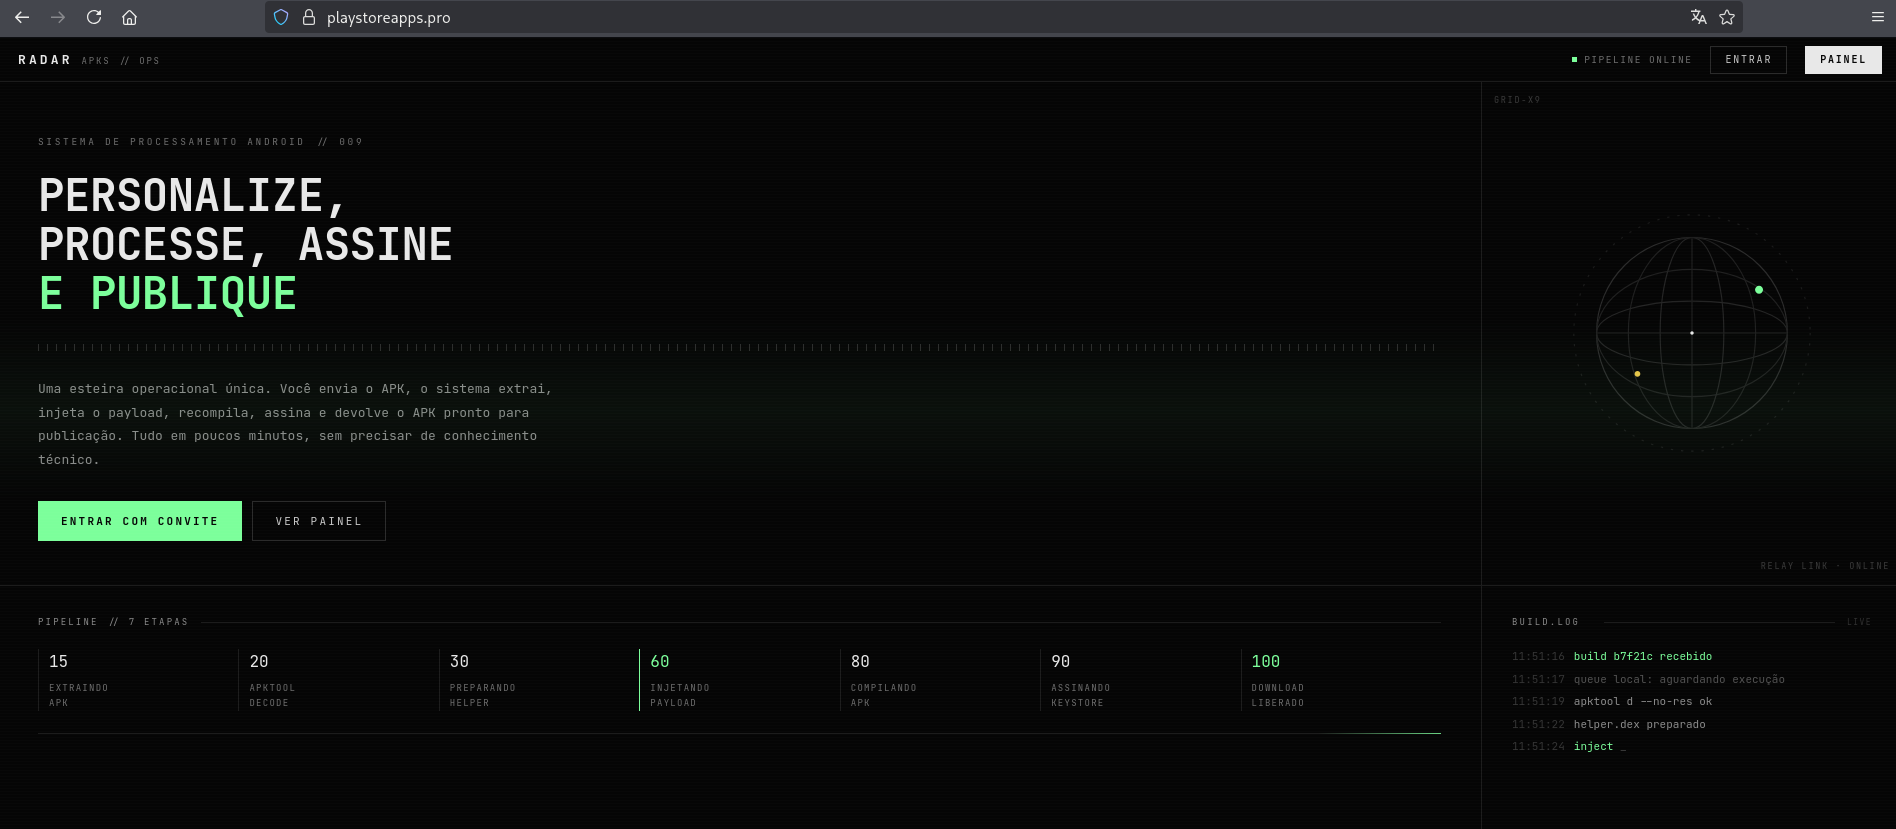
*Figure 20: The RADAR platform at *playstoreapps\[.\]pro*, showing a live 7-stage build pipeline from APK extraction through payload injection to signed download.*
The admin panel, accessible with factory-default credentials that were never changed, reveals the operational scale: three active accounts, two at "VIP Elite" tier, and nine builds processed on the day we observed it. The platform supports user management with tiered access, build quotas, and invite-based onboarding, the same franchise infrastructure pattern we've seen throughout this ecosystem.
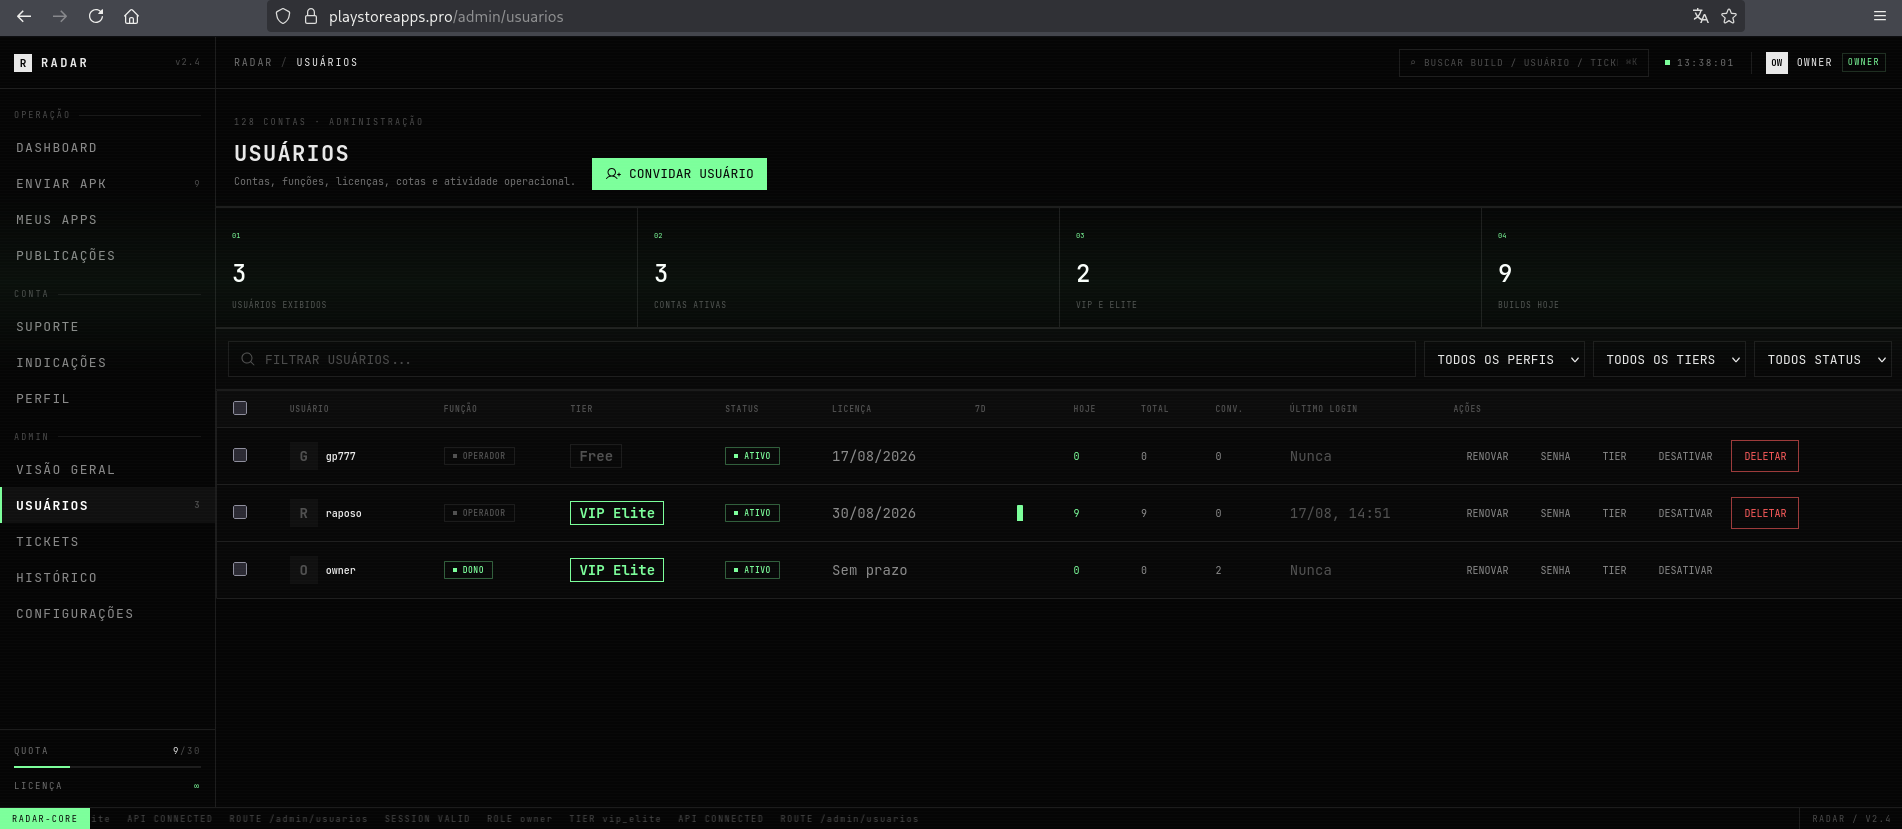
*Figure 21: RADAR's admin panel showing three operator accounts, tiered licensing, and daily build counts.*
The app list inside the panel shows what these operators are building: package-tracking lures (Jadlog, Movimente Express), health insurance (Amil), loyalty programs (Livelo), government services (MeuINSS), and generic configuration prompts, all tailored to Brazilian targets.
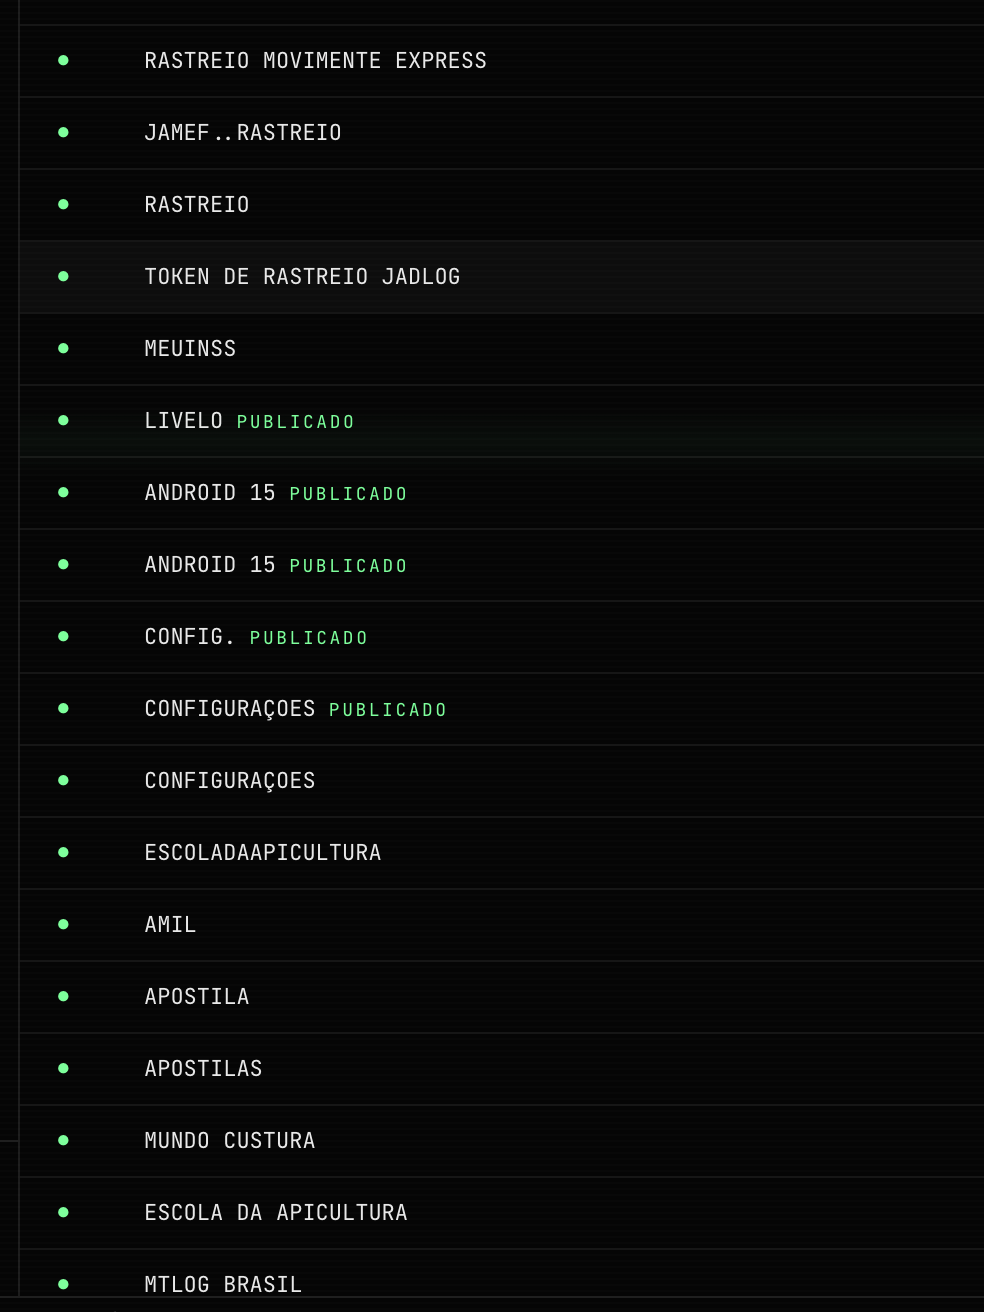
*Figure 22: The operator's app inventory: Brazilian shipping, insurance, loyalty, and government lures, some marked as published.*
Nine builds in a single day, from a platform with three accounts and default credentials. The barrier between "I want to run a campaign" and "I have a signed, weaponized APK" is a drag and a drop.
## A Real-World Delivery, Observed
During an incident response engagement, we observed a BTMOB operator targeting customers of a major Brazilian retail chain. The attack chain was a multi-stage social engineering operation delivered entirely through WhatsApp, combining automated messaging with live voice interaction, a level of operational sophistication that goes well beyond a mass-phishing blast.
### Stage 1: Precision Targeting
The initial contact arrived via WhatsApp from a profile configured with the retailer's official branding and logo. The message, formatted as an "Assistente Virtual" (Virtual Assistant), opened by displaying the victim's full name, membership number, national ID (CPF), date of birth, phone number, and current plan tier, all accurate.
This level of precision suggests access to previously compromised databases or data aggregated from multiple Brazilian breach dumps. The effect is immediate: seeing your own data quoted back at you by what looks like an official channel erases skepticism before it forms.
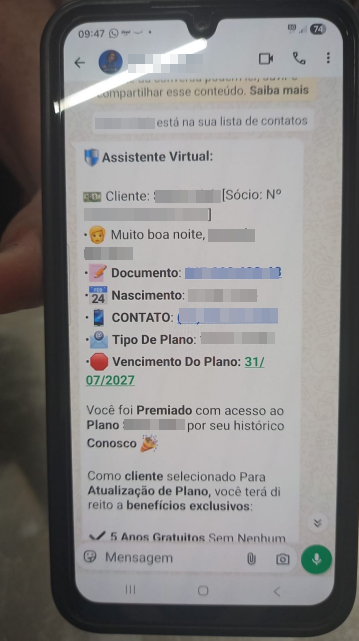
*Figure 23: The initial contact: a spoofed *"Virtual Assistant"* quoting the victim's personal data to establish credibility.*
### Stage 2: The Offer
The message then presented a fake loyalty upgrade, a premium tier with fabricated benefits: five free years, a 20% discount on partner stores, and priority access to offers. The victim was given a binary choice: (1) Accept or (2) Decline. An internal reference code **(`IFBM0I`)** was embedded in the message, suggesting the operator runs a campaign-tracking system across victims.
The structure mirrors a legitimate customer-service interaction so closely that declining feels like opting out of a real benefit.
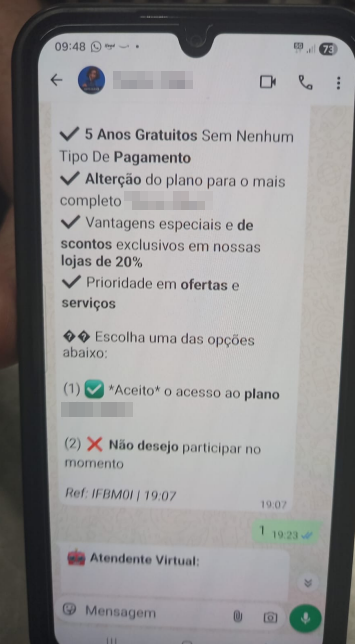
*Figure 24: The fake loyalty offer with a binary accept/decline prompt and an internal campaign-tracking reference code.*
### Stage 3: The Call, Then the Payload
After the victim accepted, the "Virtual Assistant" announced that an attendant would call to "activate" the new plan. A six-minute voice call followed. This is the critical step. The call serves three purposes: it humanizes the interaction, it gives the operator a chance to walk the victim through enabling "unknown sources" on their Android device, and it creates enough urgency to push the victim past any remaining hesitation.
Minutes after the call ended, a 4.1 MB `.apk` file was delivered directly via WhatsApp. Once installed through sideloading, the dropper initiated the BTMOB RAT infection cycle.
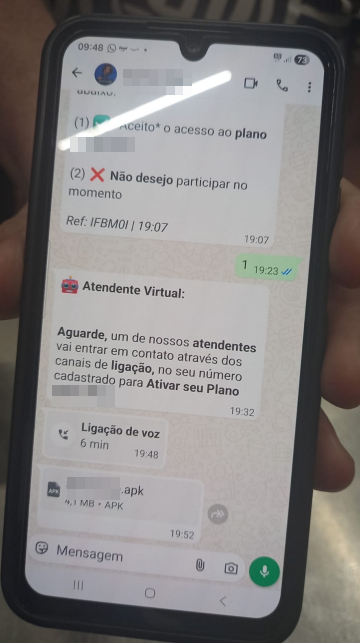
*Figure 25: Post-call payload delivery: a *4.1 MB APK sent via WhatsApp* after a six-minute vishing call.*
### What This Shows
This is not a spray-and-pray campaign. The operator had the victim's real data before contact, used a spoofed brand identity, ran a scripted social engineering flow with a reference-tracking system, deployed a live caller to handle objections and enable sideloading, and delivered the payload through WhatsApp, a channel most security tools don't inspect. Each stage was designed to erode one more layer of doubt.
### A Different Vector: The Fake Play Store
During our research into BTMOB delivery mechanisms, we identified a second distribution channel operating alongside the WhatsApp campaigns: a near-perfect clone of the Google Play Store hosted at **`playstoreap[.]lovable[.]app`.**
The site replicates the Play Store's layout, branding, and install flow, serving spoofed pages for popular Brazilian apps: Nubank, TikTok, and even a fake Gov.BR government service. Each page displays fabricated ratings and download counts to build trust, though the cracks are visible: zero reviews, no descriptions, and every app categorized as "Other."
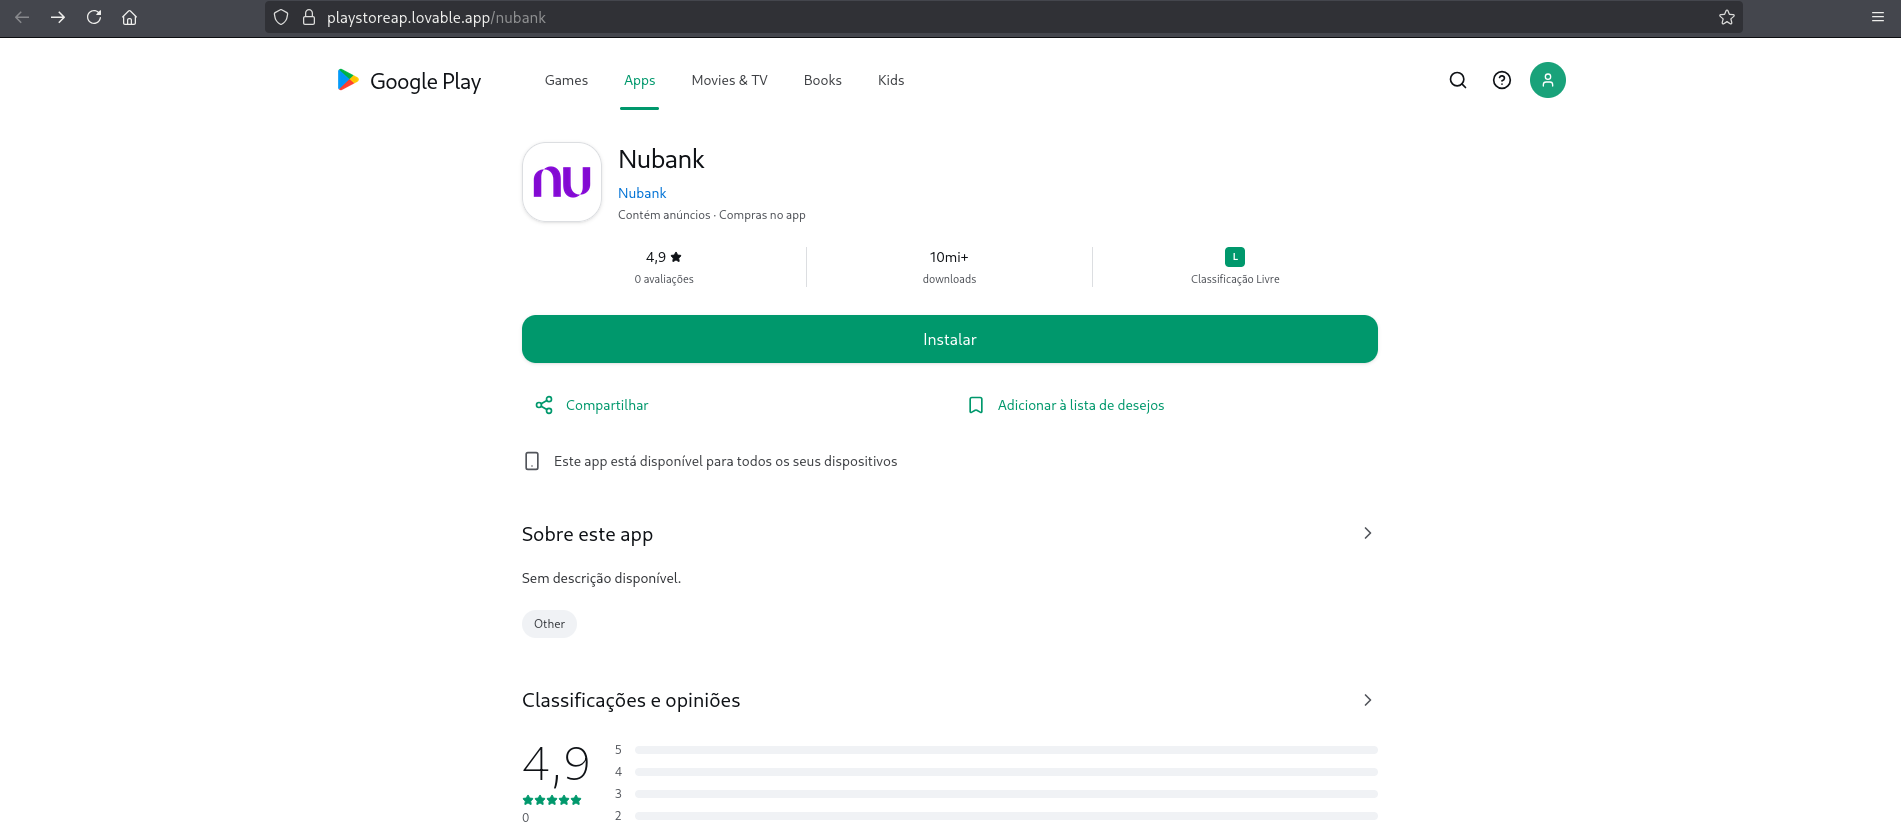
*Figure 26: Fake Play Store page impersonating *Nubank* at *playstoreap\[.\]lovable\[.\]app*. Note the fabricated 4.9 rating with zero reviews.*
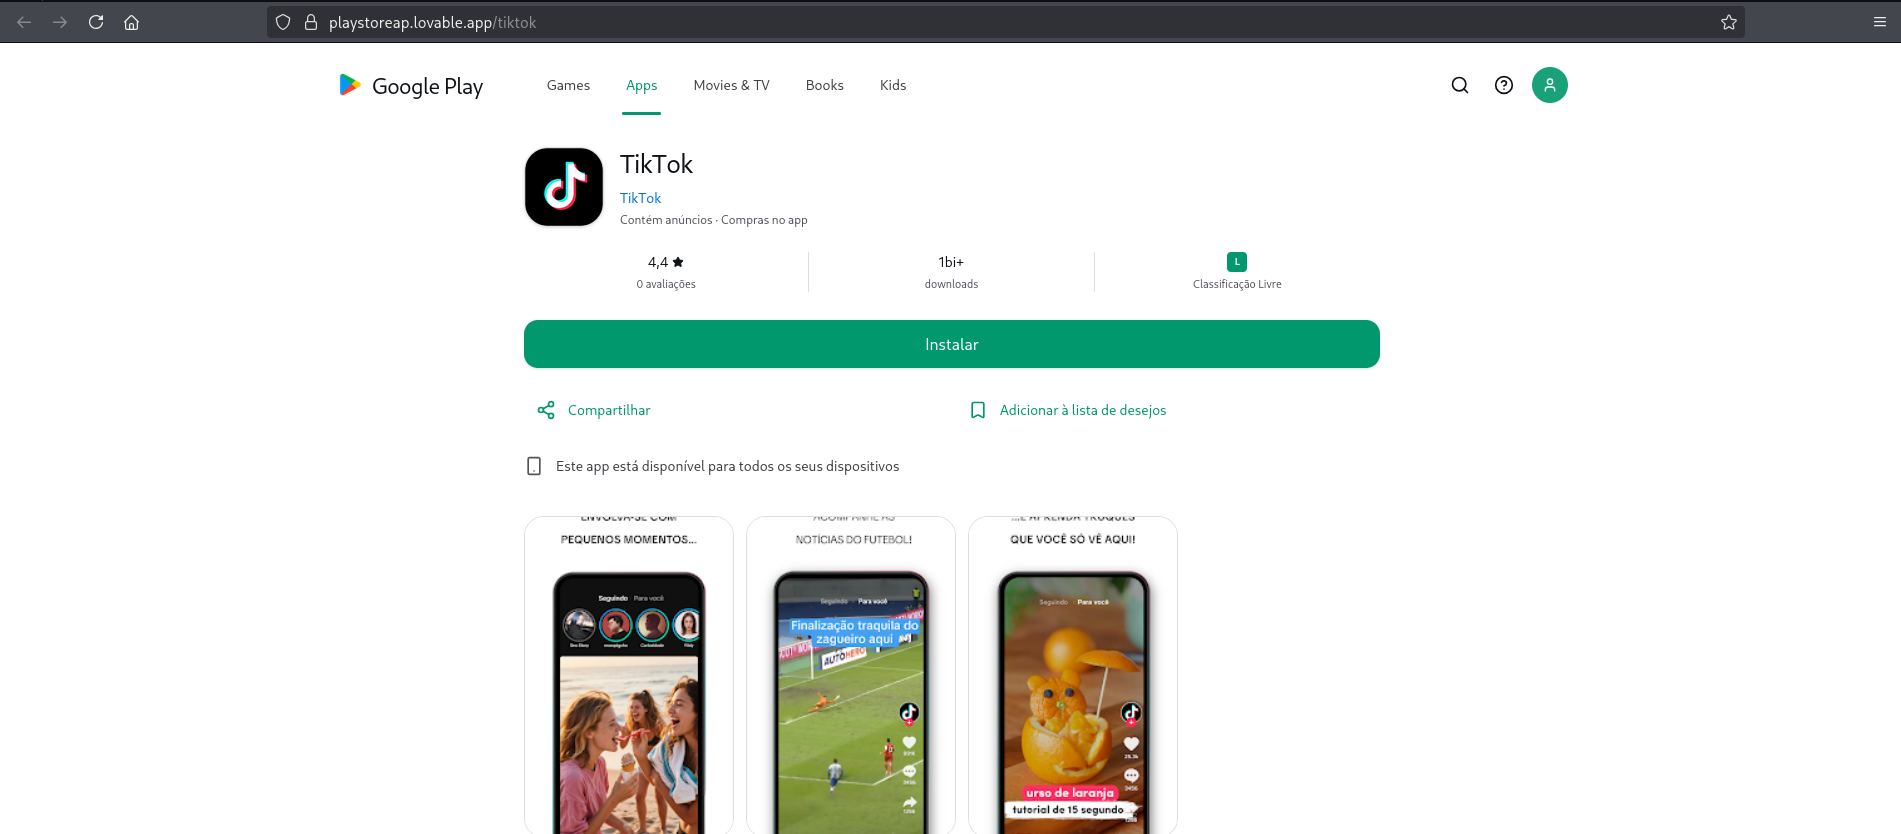
*Figure 27: The same fake store serving a spoofed *TikTok* page: mixing financial and social-media lures to broaden the target pool.*
The store's landing page reveals the operator's full inventory, including a **GhostNFC** entry, an NFC relay tool from the same Brazilian fraud ecosystem where BTMOB circulates.
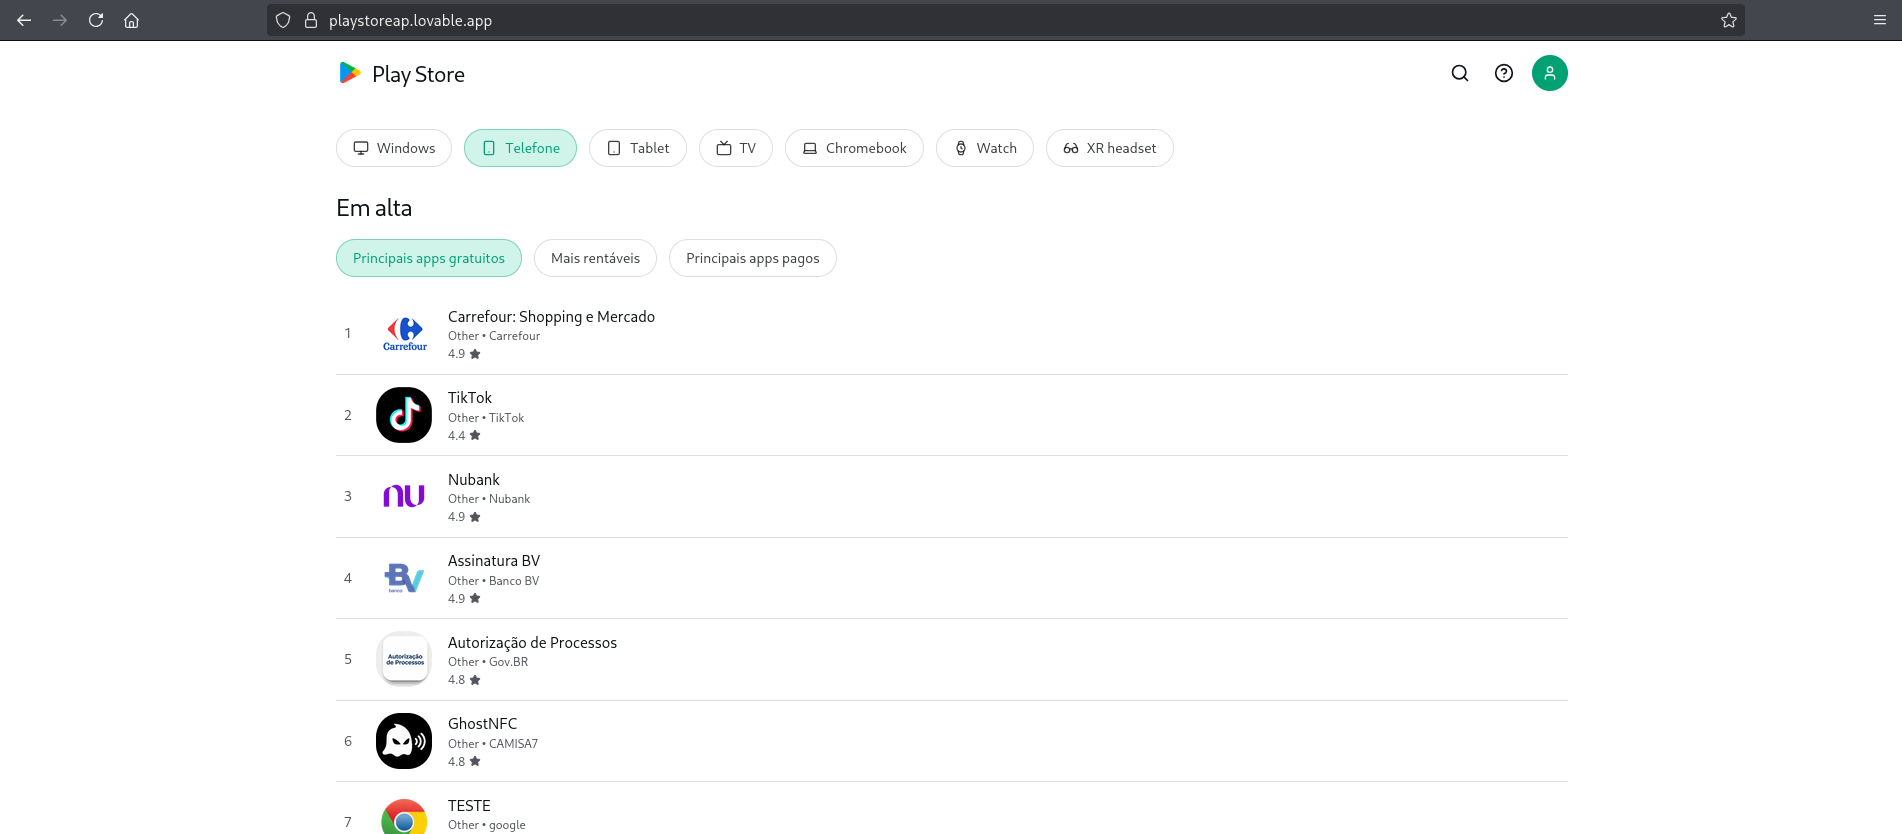
*Figure 28: The fake store's trending page, exposing the full app inventory including *GhostNFC* and an unfinished test entry.*
The hosting is worth noting: **`lovable[.]app`** is a legitimate app-building platform, giving the clone a valid TLS certificate and a clean domain reputation. A victim sees a padlock, a **`.app`** domain, and a green install button. Nothing to flag. Following our research, the QuimeraX team reported the site to Lovable's Trust & Safety team, and the fake store was taken down.
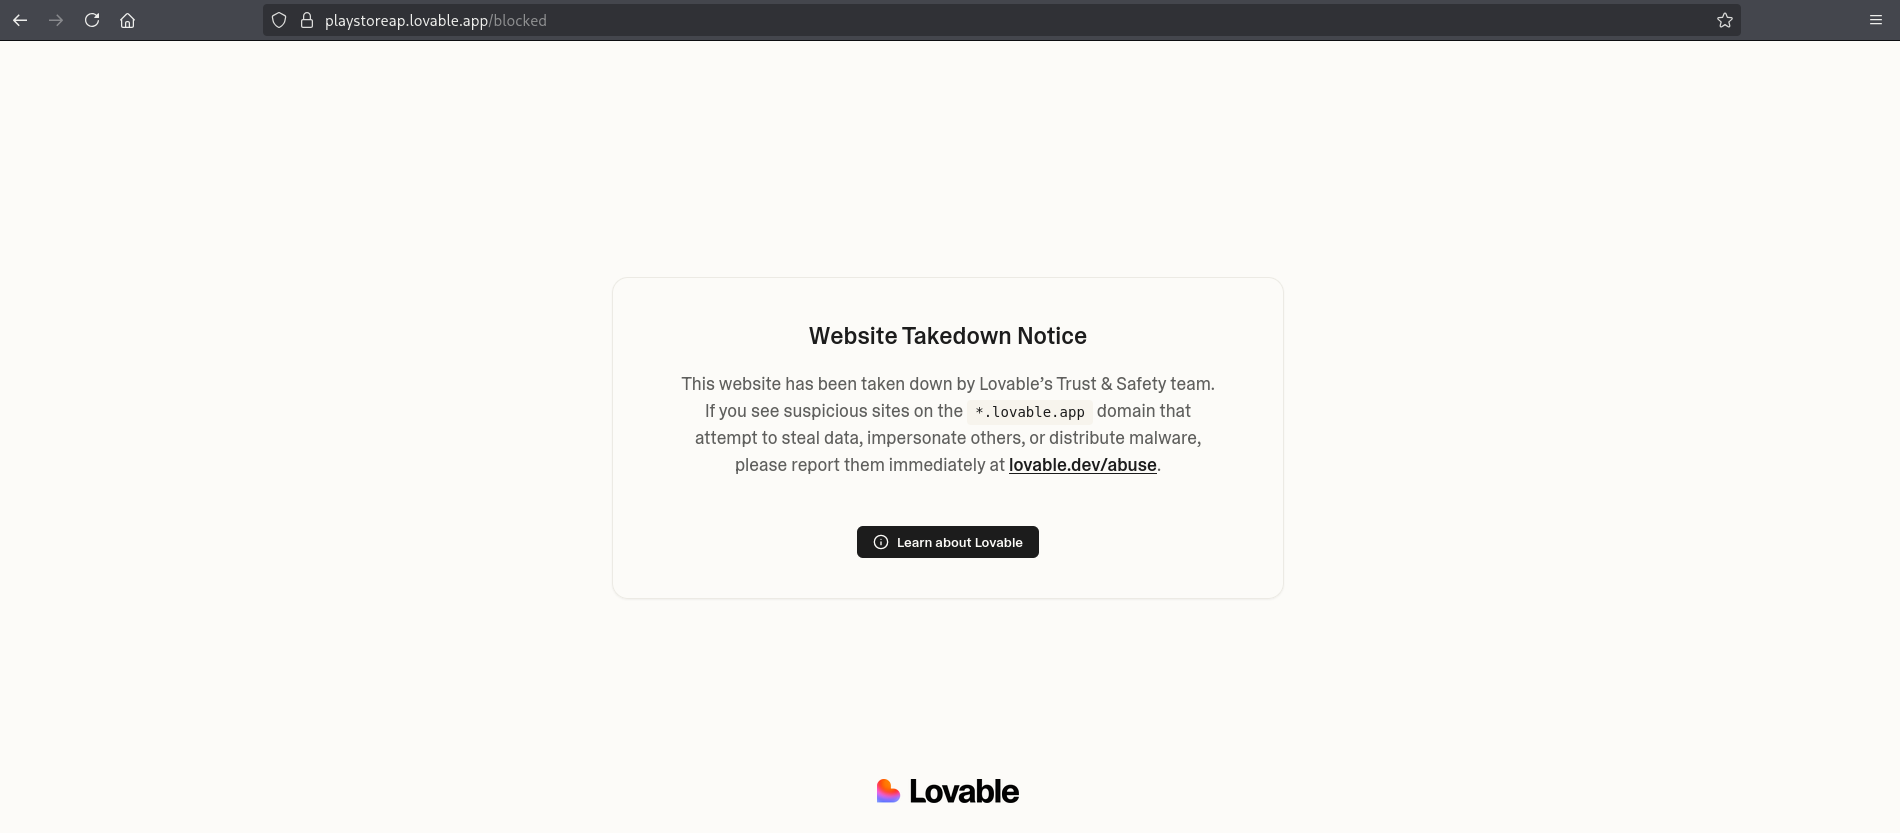
*Figure 29: Takedown notice at *playstoreap\[.\]lovable\[.\]app* after *QuimeraX* reported the fake Play Store to Lovable's Trust & Safety team.*
## What This Means
BTMOB is not exceptional because of any single capability. Every feature it offers exists in other malware families. What makes it significant is the completeness of the package and the business model wrapped around it.
From a single developer in Syria building CypherRAT for a Telegram audience of script kiddies, to a source-code-available franchise with reseller APIs, USDT payments, automated APK generation, and third-party contributors adding bank-specific bypasses, BTMOB's evolution mirrors the professionalization of the broader cybercrime ecosystem. The developer doesn't need to attack banks. The developer sells the tools, collects subscriptions, and lets a growing network of independent operators handle the risk.
For defenders, the implications are clear. Domain-based blocking fails because there is no single C2 domain; each operator runs their own infrastructure. The same IOCs appear across unrelated campaigns because crypto constants, wire delimiters, signing keys, and User-Agent strings are baked into the source code and shared by all operators. And the source code is freely available, which means the barrier to entry is a YouTube tutorial and a Windows VM.
The good news: BTMOB's crypto scheme hasn't changed since v2.5\. The testkey signing is a reliable anchor. The **`yarsap_*`** naming convention and **`yaarsa/`** directory structure are stable.
The platform will continue to fragment. More variants, more operators, more regional adaptations. But the "DNA" is identifiable. You know what to look for.
### BTMOB is one campaign. The ecosystem behind it is much larger
Malware families, leaked source code, reseller networks, and exposed infrastructure are constantly reshaping the threat landscape. QuimeraX helps organizations uncover these connections, track the actors behind them, and turn fragmented signals into actionable intelligence.
If you want to understand which threats are targeting your organization and what infrastructure, actors, and campaigns are connected to them, talk to QuimeraX.
**[→ Talk to our Threat Intelligence team](https://quimerax.com/en?ref=blog.quimerax.com)**
## Indicators of Compromise
### Infrastructure Fingerprints
| Indicator | Value |
| -------------------------------- | ---------------------------------------------------------------------------- |
| Shodan dork (C2) | http.html\_hash:-983012381 port:3000 |
| Shodan dork (Bypass panels) | html:"painel de controle elite" |
| html\_hash (fake 403, port 3000) | \-983012381 |
| C2 port signature | 80 (IIS), 3000 (Node.js/Express), 3306 (MySQL), 8080 (WebSocket), 3389 (RDP) |
### Network Indicators
| Pattern | Where to look |
| ------------------------------------------------------- | ----------------- |
| HTTP POST to /yaarsa/private/yarsap\_\*.php | IDS/proxy logs |
| WebSocket JSON with idf, sidf, cip, itype:"Slr\_client" | Port 8080 traffic |
| WebSocket connection to ws://:8080/con | Port 8080 traffic |
| 426 Upgrade Required on port 8080 | HTTP response |
### Domains
| Domain | Context |
| -------------------------------------- | ---------------------------- |
| btmobrat\[.\]net | Official storefront |
| playstoreapps\[.\]pro | RADAR bypass platform |
| playstoreap\[.\]lovable\[.\]app | Fake Play Store distribution |
| rastrear-encomendas2\[.\]pages\[.\]dev | Fake Rodonaves distribution |
| meusdownloads\[.\]site | Fake Play Store distribution |
### IPs
| IP | Context |
| ------------------------- | ------------------- |
| 77\[.\]111\[.\]101\[.\]24 | Confirmed C2 server |
> **Note:** The IP listed above is one confirmed example. The Shodan query **`http.html_hash:-983012381 port:3000`** returned **1,402** hosts at the time of writing. Use the queries in the Infrastructure Fingerprints table above to find current results.
### C2 Backend Paths
| Path | Function |
| ---------------------------------- | ------------------------------------------------------------ |
| /yaarsa/private/yarsap\_85401.php | Master config (DB creds, crypto keys, User-Agent validation) |
| /yaarsa/private/createacc.php | Account creation API (reseller-authenticated) |
| /yaarsa/user/loginbt.php | Operator login panel |
| /yaarsa/user/loginbt3.php | Operator login with Google Authenticator 2FA |
| /yaarsa/user/login.php | Decoy (fake 403 redirect) |
| /yaarsa/index.php | Decoy (fake 403 redirect) |
| /yaarsa/server/websocket-server.js | Node.js/Express + WebSocket server |